Solutions
Start from what you need
or from who you are.
One read-only platform for every cloud you connect: harden it against the CIS benchmarks, review who has access, spot unused licences and prove your configuration to an auditor.
What are you trying to do?
Cloud Security Posture Management (CSPM)
Fix risky misconfigurations across your cloud.
Every connected cloud checked against the CIS benchmarks, with evidence and a severity estimate for each finding.
Explore Cloud Security Posture Management (CSPM) →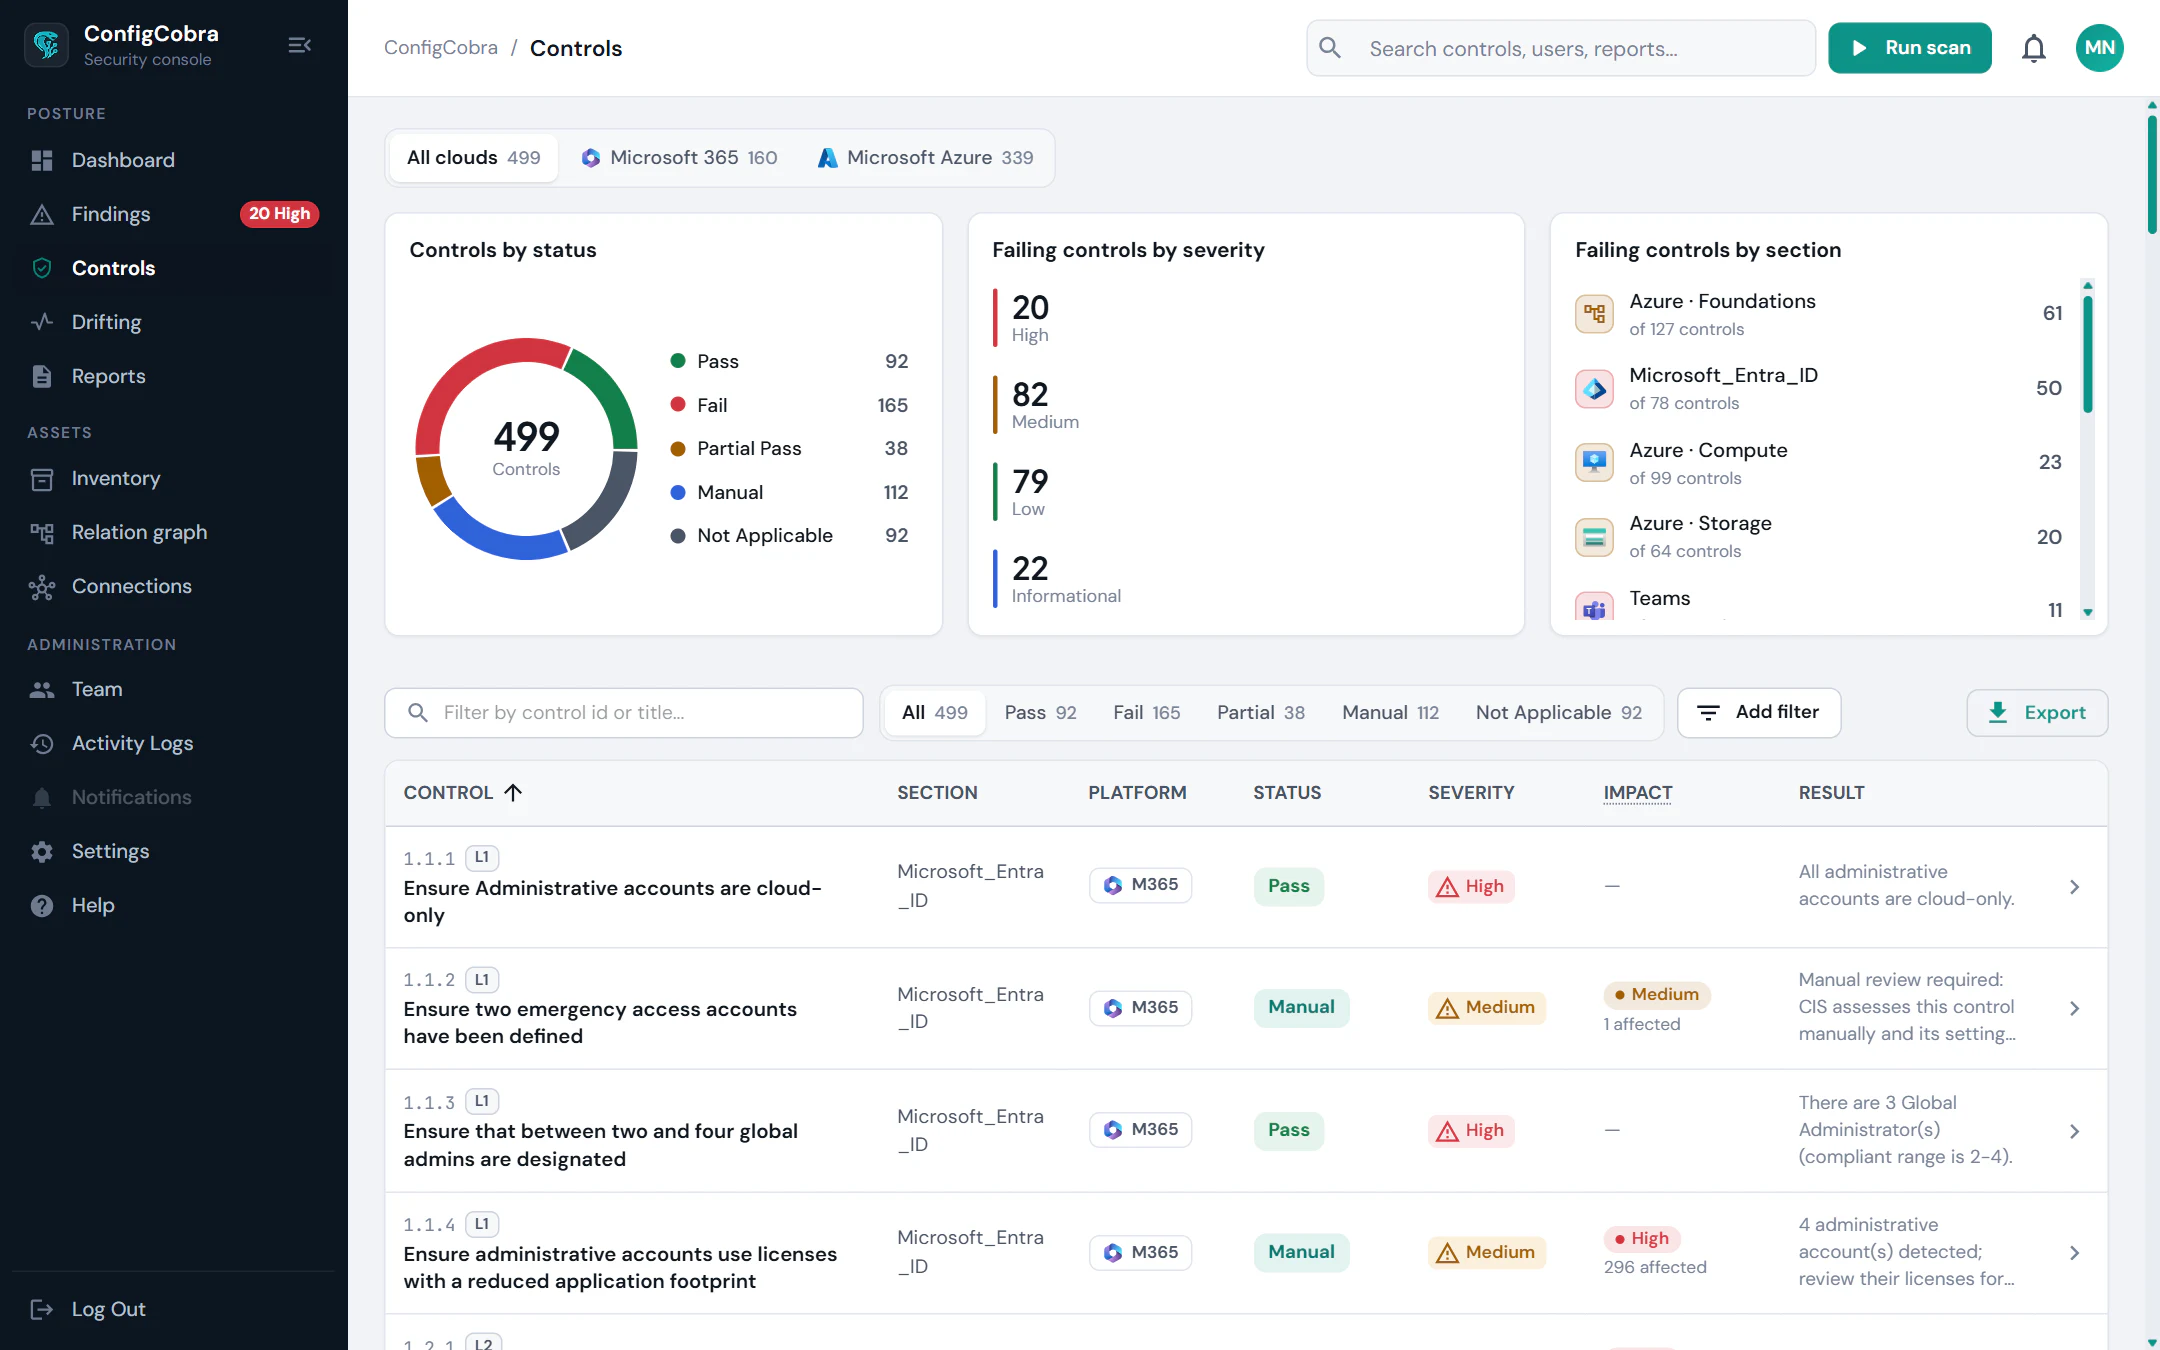
Identity & Access Governance
Find inactive users, guests, admins and risky apps.
Built-in risk views list stale accounts, guests who never signed in, users without MFA and high-privilege apps.
Explore Identity & Access Governance →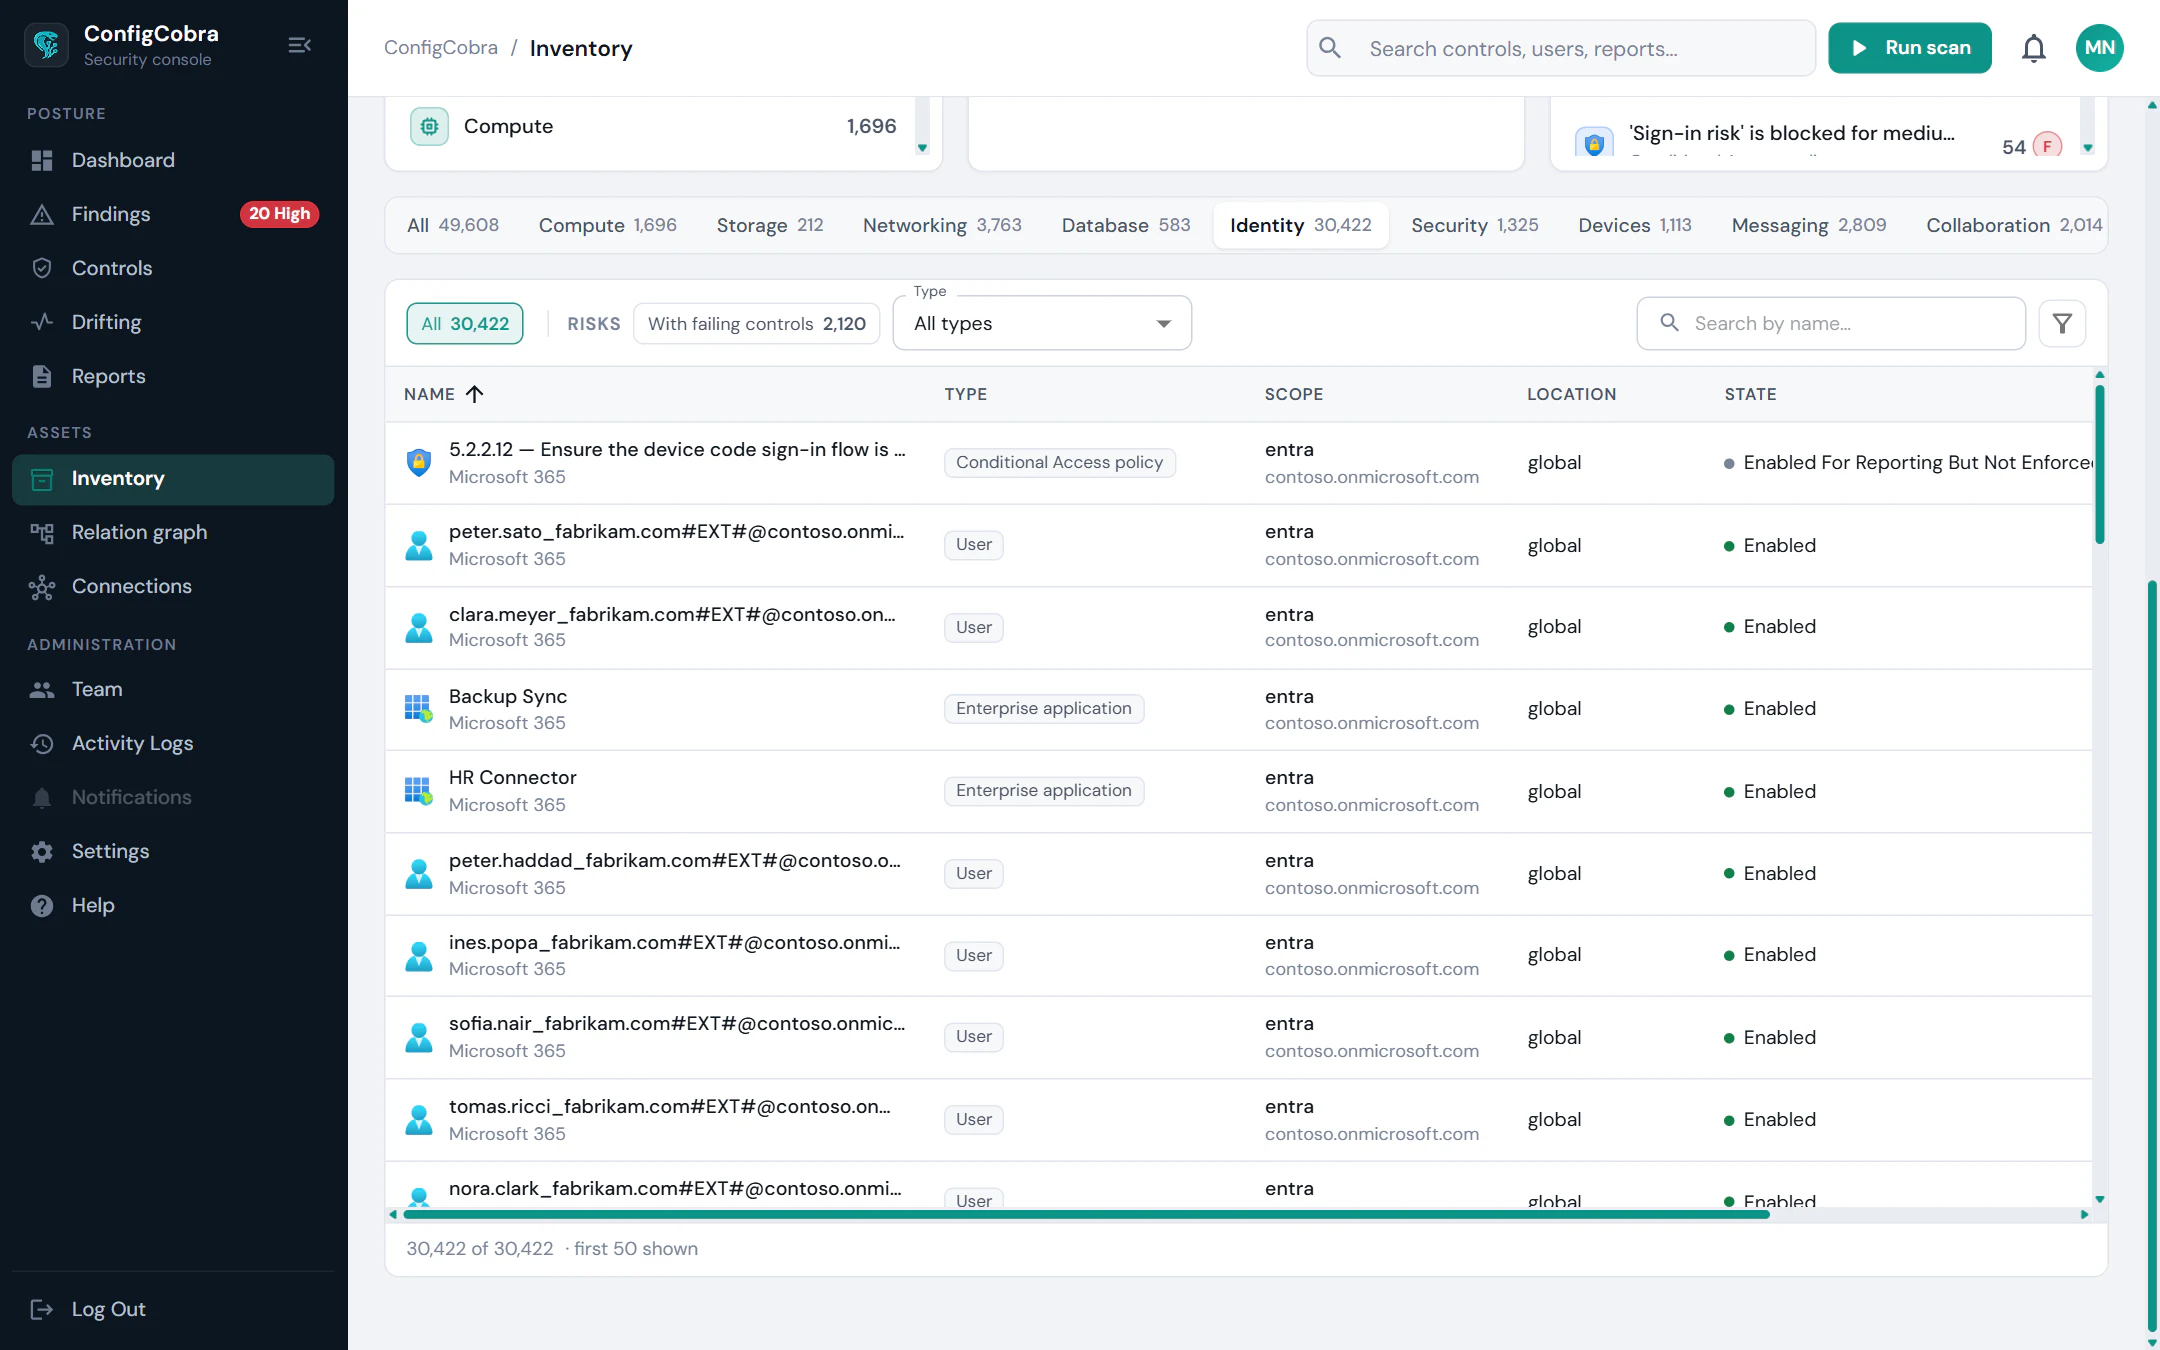
Cost & License Optimization · Partly available
Spot unused paid licences and unattached disks.
The same read-only inventory you use for security lists unused paid licences and unattached disks.
Explore Cost & License Optimization →Audit & Evidence
Prove your configuration to an auditor or a client.
A dated PDF report with evidence, an evidence export and a read-only seat for your auditor or client.
Explore Audit & Evidence →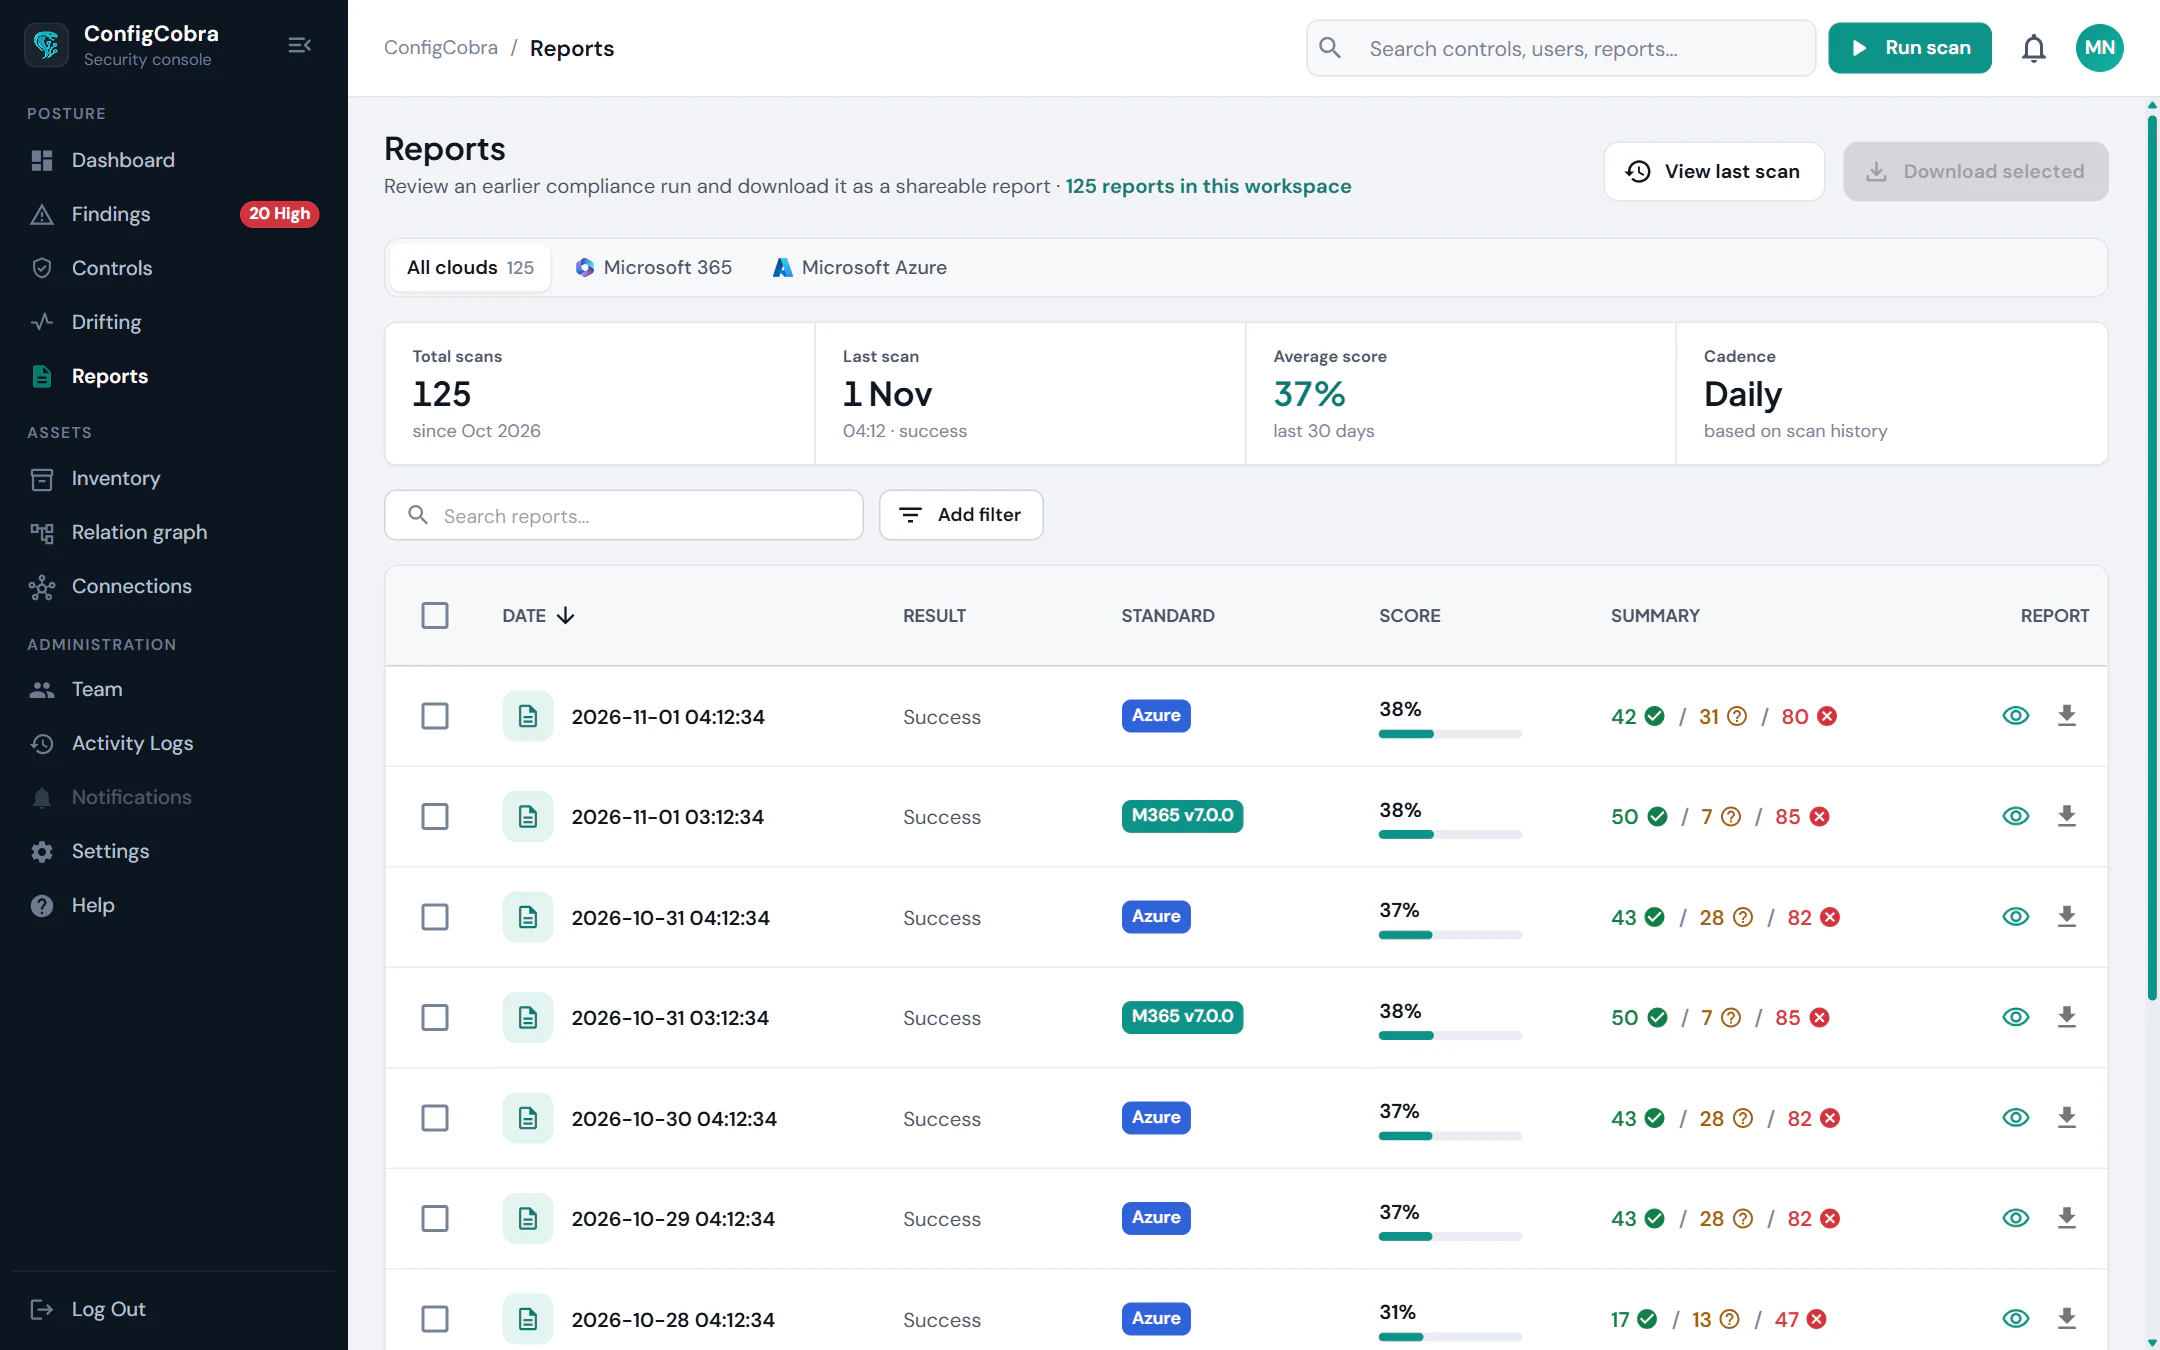
Who are you?
- For MSPsAssess every client tenant from one workspaceSee how it works for you →
- For Auditors & consultantsEvidence, timestamped snapshots and a read-only seatSee how it works for you →
- For IT & security teamsFind, prioritise and safely fix misconfigurationsSee how it works for you →
- For CISOsA posture score and a PDF report you can take to the boardSee how it works for you →
Not sure where to start?
Start a 14-day free trial with full access, or tell us what you need and we will send a quote.