Connector · Microsoft Azure
CIS benchmarks for Azure.
Read-only. Per resource.
ConfigCobra scans your Azure subscriptions against four CIS Microsoft Azure benchmarks — 339 controls — in one read-only scan, and points every finding at the exact resource.
- CIS controls
- 339
- CIS Azure benchmarks
- 4
- Access
- Read-only
- Findings
- Per resource
Four CIS Azure benchmarks. One scan.
Foundations v6.0.0 plus Compute, Database and Storage Services v2.0.0: 205 Level 1 and 134 Level 2 controls.
See the benchmark breakdown →Every subscription, every resource.
Scan every subscription the app can read, or a selected list. One tenant per scan.
Connect
Reader on your subscriptions. Nothing more.
An Entra app registration with a certificate, Reader on the subscriptions you choose and a read-only Microsoft Graph policy permission. ConfigCobra never writes to your Azure.
Foundations
127 Foundations controls, section by section.
The Foundations v6.0.0 benchmark runs from Analytics Services to Storage Services, with Security Services the largest section at 38 controls.
Foundations sections →Inventory
Every resource, with the properties that matter.
Resources across your subscriptions with security properties such as public network access, minimum TLS and Key Vault secrets without expiry, linked to their findings.
Explore the inventory →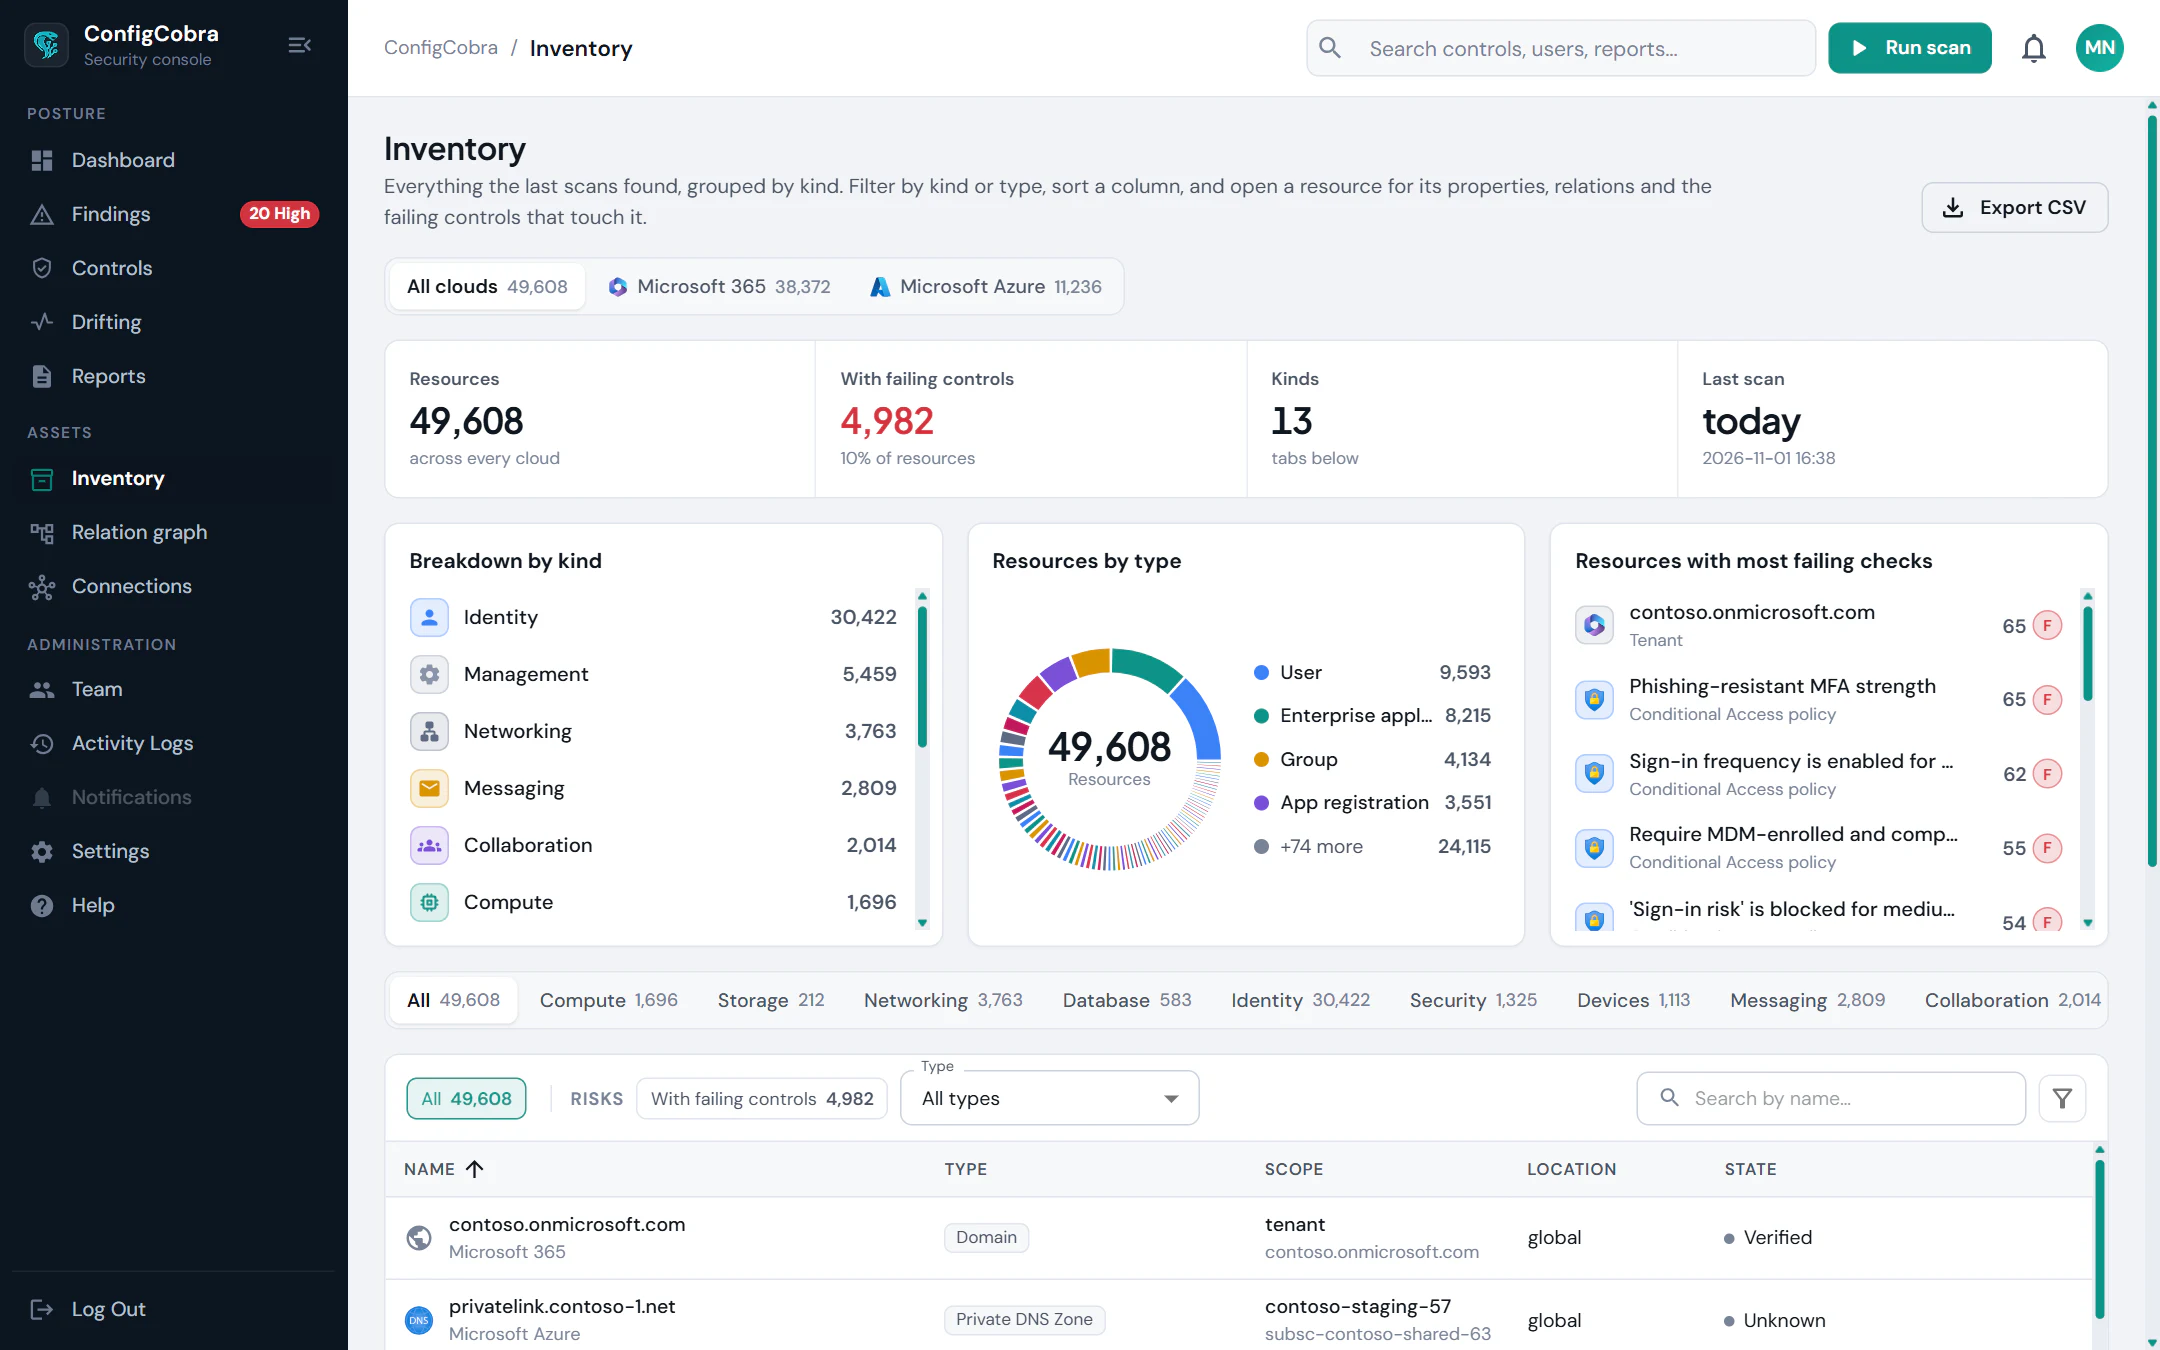
Impact
See what a fix changes before you apply it.
For a failing control, ConfigCobra lists the resources and identities the fix would affect, with an impact level, so nothing breaks by surprise.
Remediation impact analysis →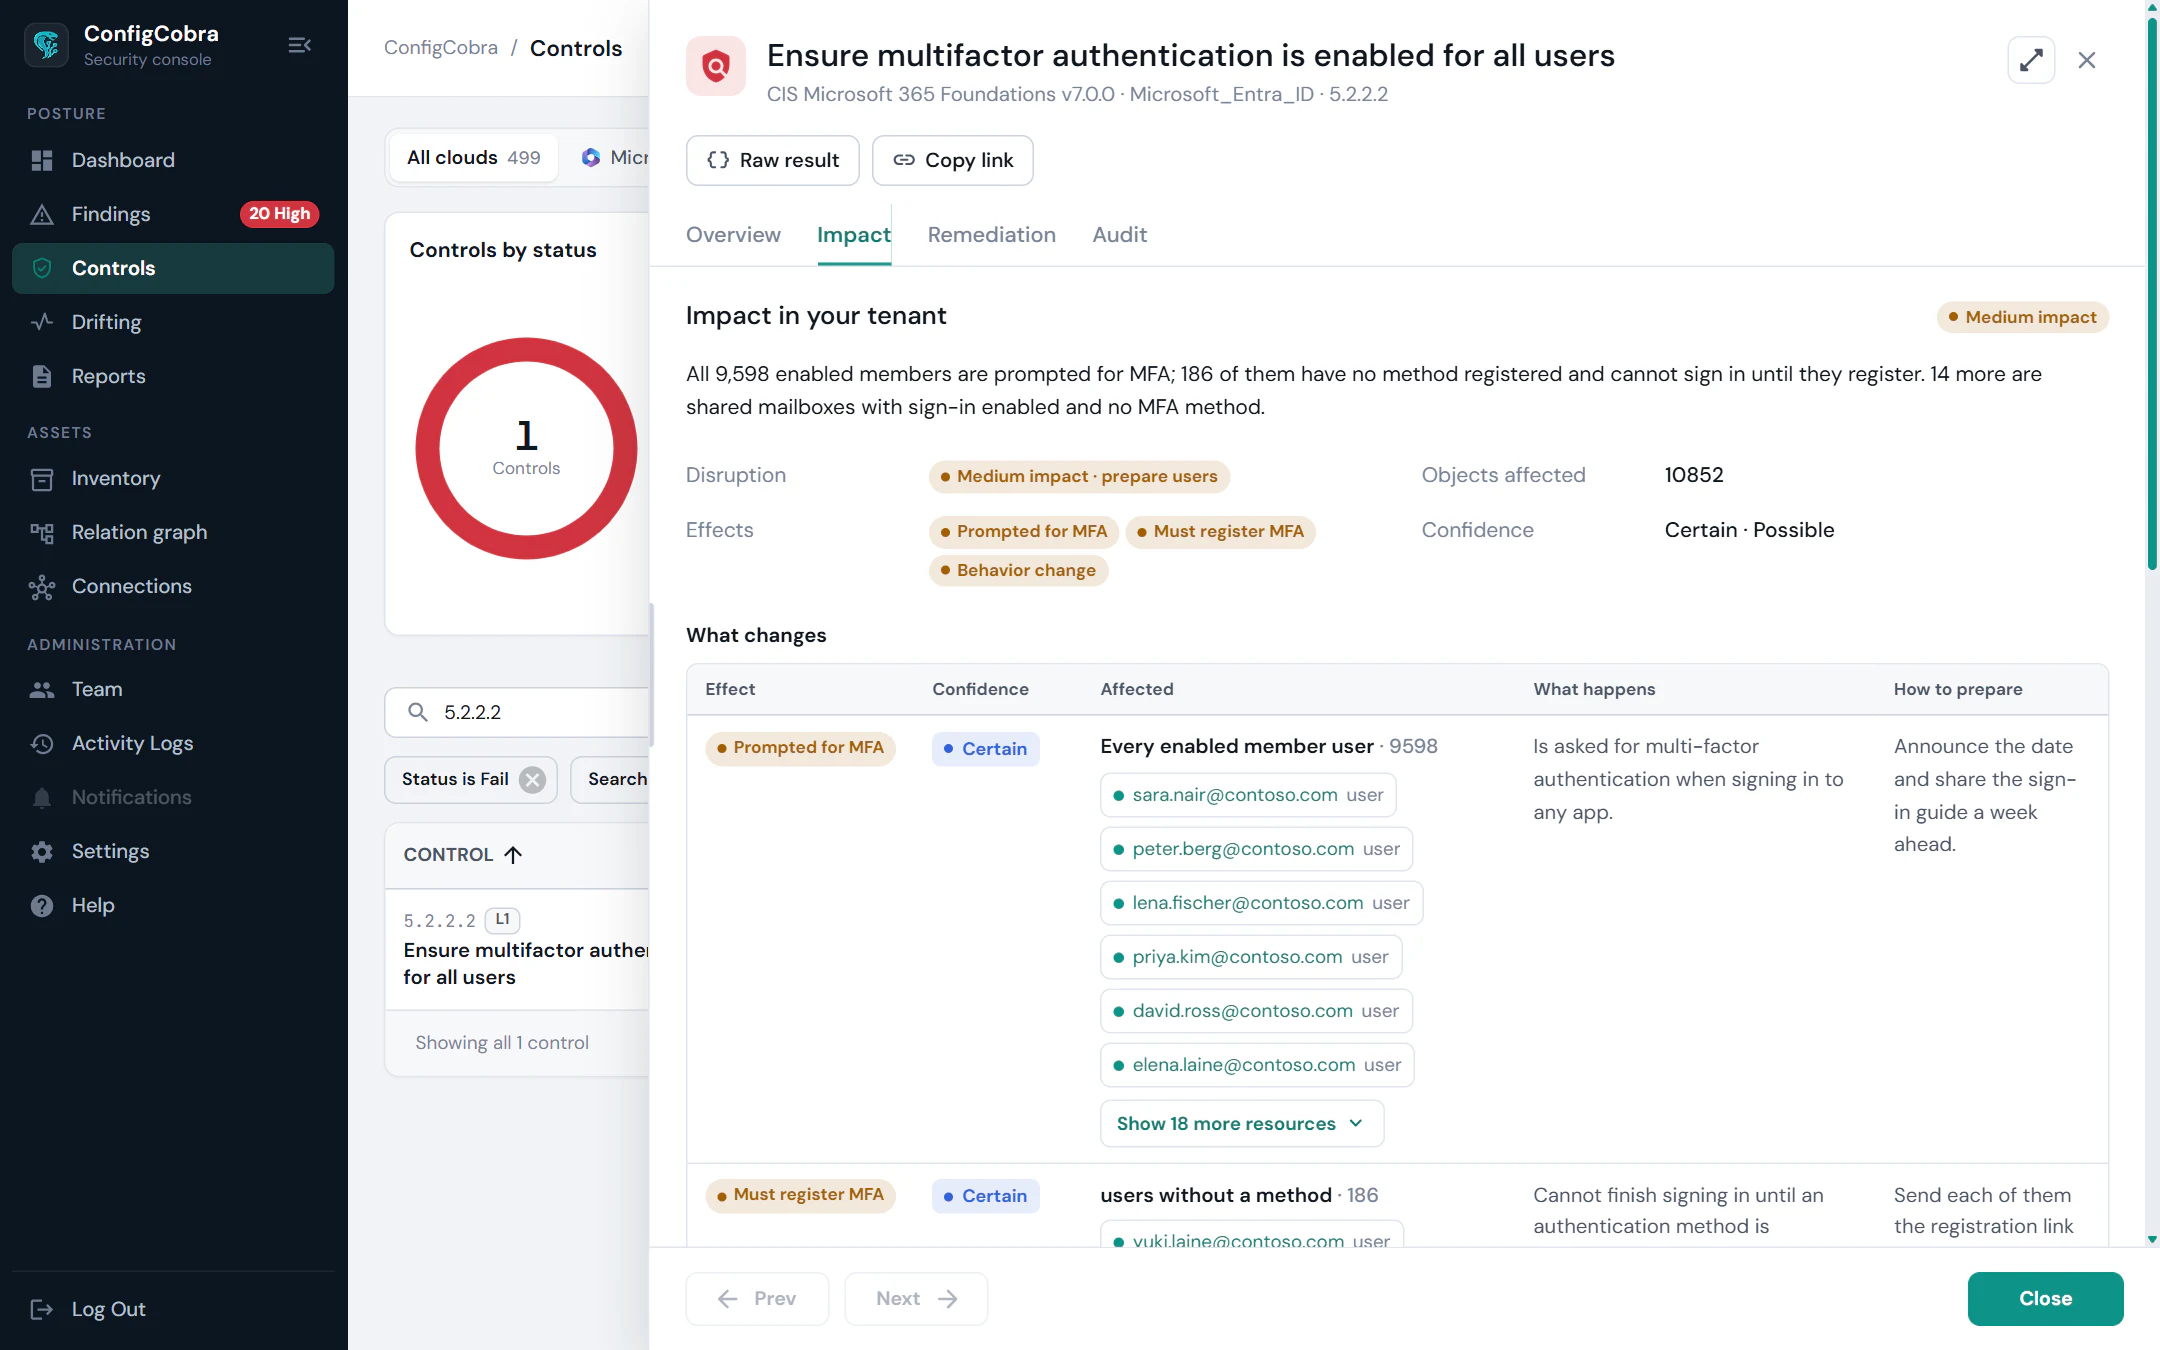
Read-only. Never writes to your Azure.
An Entra app registration that authenticates with a certificate — no client secret.
- Target subscriptions
ReaderReads resource configuration in the subscriptions you choose.
- For Key Vault checks
Key Vault ReaderAdded for the Key Vault checks.
- Microsoft Graph
Policy.Read.AllRead-only Microsoft Graph policy permission.
- Entra app registration
CertificateCertificate-based authentication — no client secret.
What you can do on Azure.
Assess your subscriptions against the CIS benchmarks and see every resource in the inventory.
- Assess
Cloud Security Posture Management (CSPM)
CIS benchmark assessment with a score, findings and a severity estimate per control
Learn more → - See
Inventory & Insights
Every user, app, device and resource in one inventory, with built-in risk views
Learn more → - Fix
Remediation
See what a fix changes in your tenant before you apply it, then use the generated script
Learn more → - Keep
Monitoring & Drift
Daily scans, drift detection and email alerts when a control regresses
Learn more → - Prove
Reports & Evidence
PDF reports with evidence and a timestamped snapshot, plus a read-only auditor seat
Learn more → - Ask
AI Assistant (MCP)
Ask your AI assistant about your posture, using live ConfigCobra scan data
Learn more →
One console for
- Microsoft 365160 CIS controls
- Microsoft Azure339 CIS controls
- Google Cloud93 CIS controls
- AWS306 CIS controls
- Google WorkspaceComing soon
Frequently asked questions
Is Azure support available?
Yes. ConfigCobra for Azure is available. Start a free trial, or ask us for a quote.
Which CIS benchmarks does ConfigCobra check for Azure?
Four CIS Microsoft Azure benchmarks: Foundations v6.0.0 (127 controls), Compute Services v2.0.0 (99), Database Services v2.0.0 (49) and Storage Services v2.0.0 (64) — 339 controls in total, all covered by one scan.
What access does ConfigCobra need in Azure?
An Entra app registration with certificate authentication (no client secret), the Reader role on the target subscriptions (plus Key Vault Reader for Key Vault checks) and the Microsoft Graph Policy.Read.All permission. Access is read-only — ConfigCobra never writes to your Azure.
Can I scan more than one subscription?
Yes. A scan can cover every subscription the app can read, or a selected list. Each scan covers one tenant.
How specific are the findings?
Every finding points at the exact Azure resource it concerns, and findings are linked to the inventory objects they relate to.
See it on your own tenant
Read-only access — ConfigCobra never changes your tenant.