Cloud Security Posture Management (CSPM)
Fix risky misconfigurations
across your cloud.
ConfigCobra CSPM checks every cloud you connect against the CIS benchmarks with read-only access. Every finding comes with evidence and a severity estimate, so you know what to fix first.
Every control, checked and explained.
The status, the severity estimate and the impact of a fix for every control on every connected cloud. Open one and the evidence is right there.
Controls Every control: status, severity estimate and the impact of a fix.
Build a hardened cloud foundation.
Read-only checks against the CIS benchmarks, with evidence for every finding. No agents, no admin password sharing.
Assess
Every CIS control, checked for you.
Connect a cloud with read-only access and ConfigCobra checks it against the CIS benchmarks for that cloud, control by control.
Browse the standards →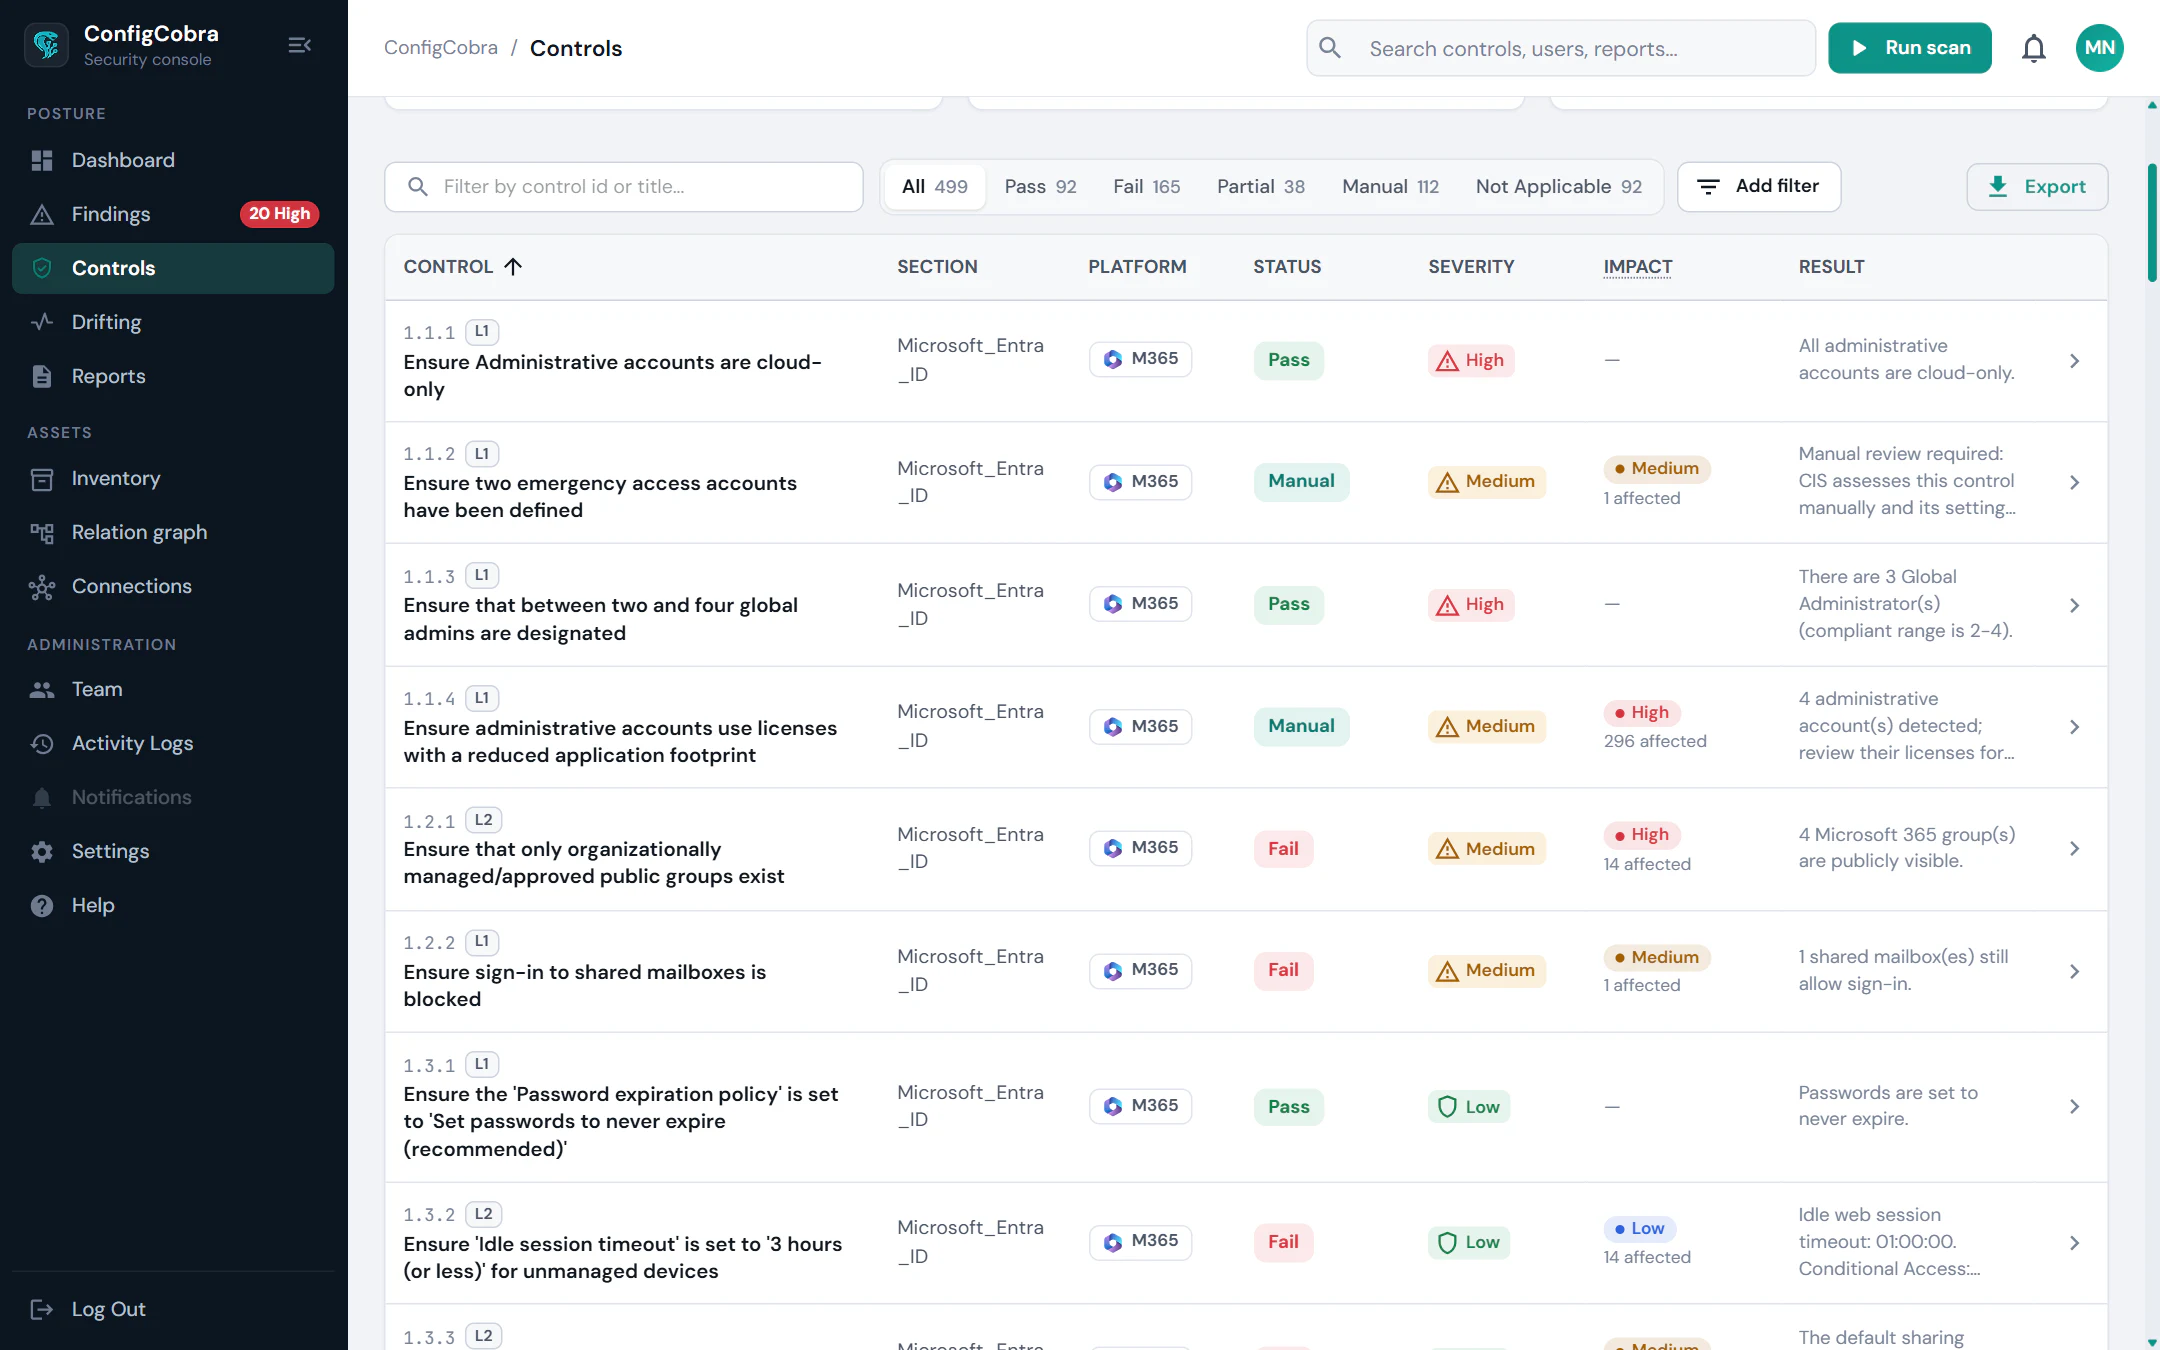
Evidence
See exactly what failed, and where.
Each finding shows the setting that failed, what the benchmark expects, what the scan found and the objects it affects.
See the connectors →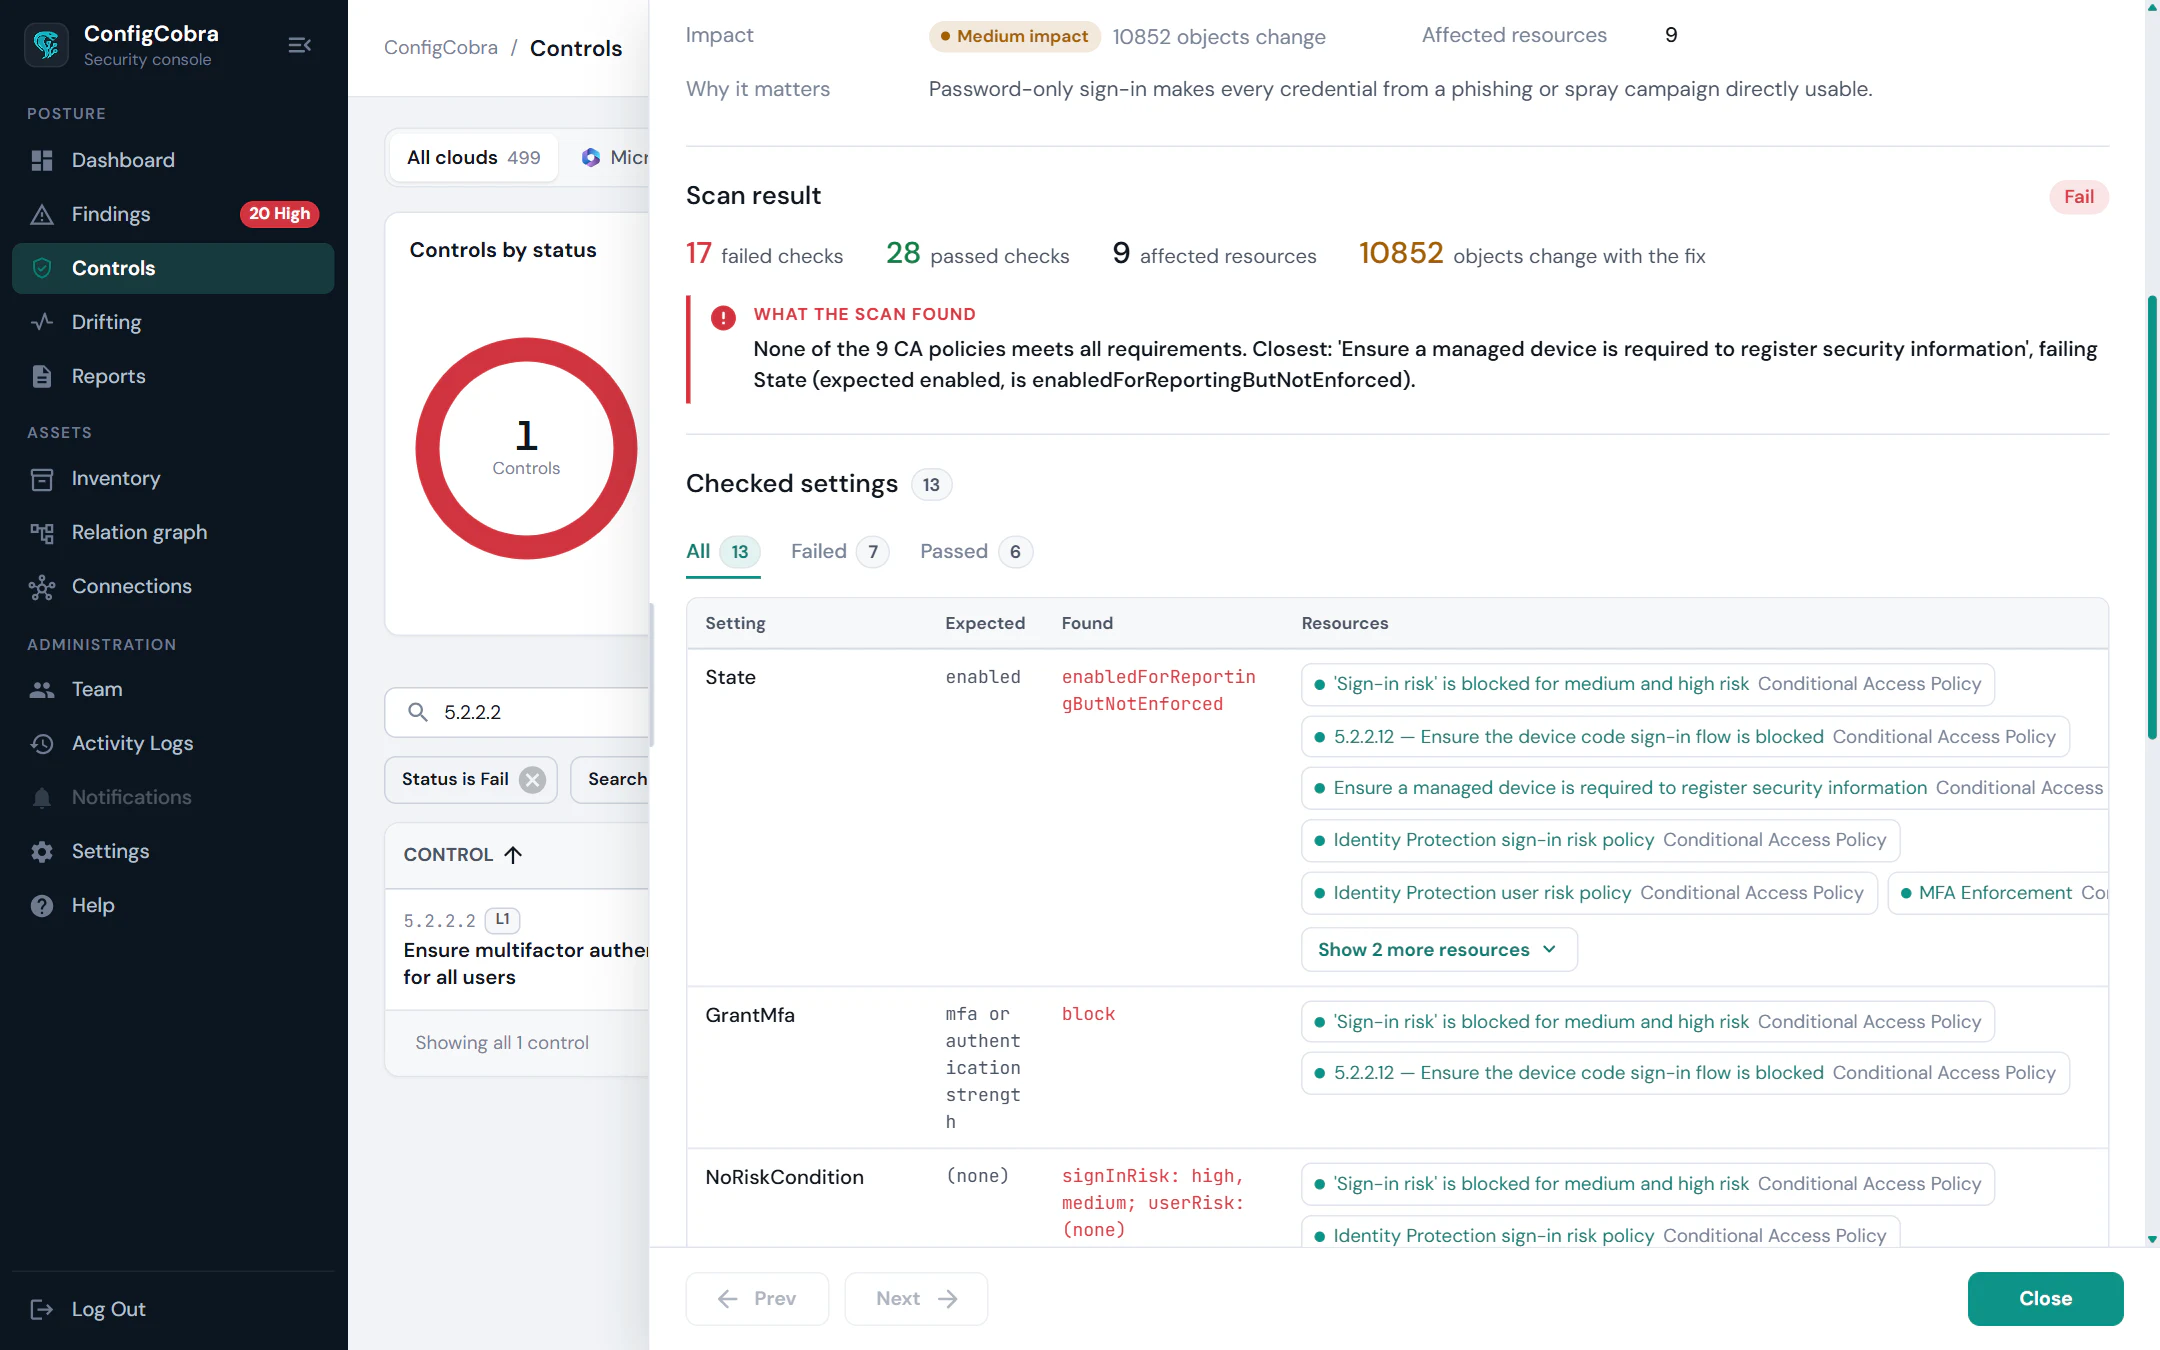
Prioritise
Know which finding to fix first.
Each control carries a severity estimate, so you know what to fix first. CIS itself publishes no severity; the estimate is ConfigCobra's.
See the impact of a fix first →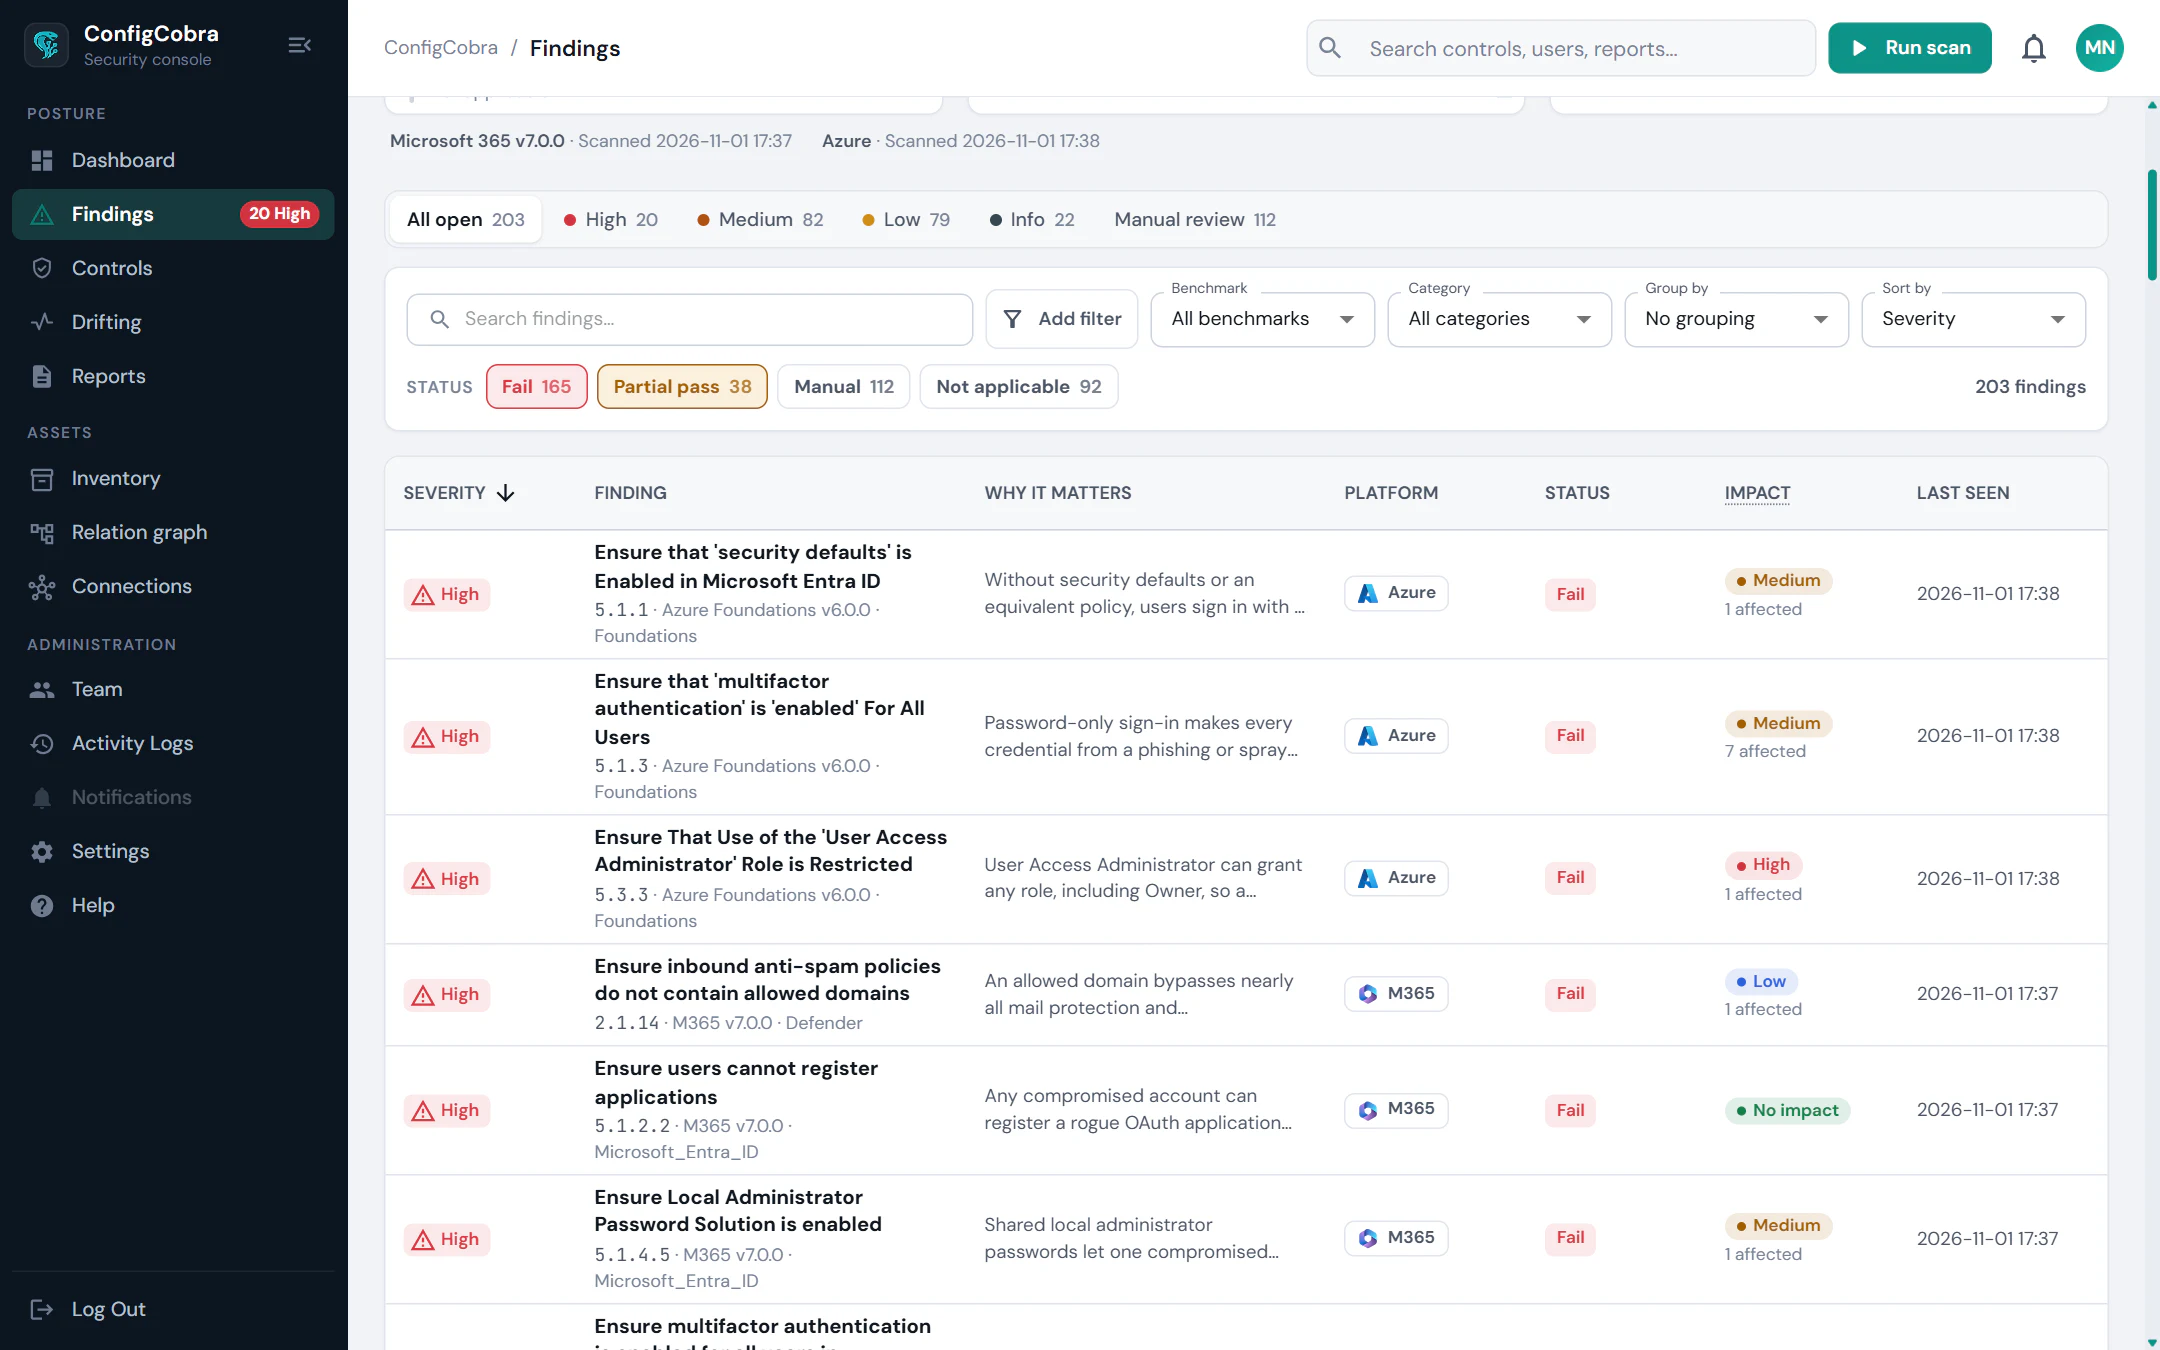
Impact
See what a fix changes before you make it.
ConfigCobra lists the users, mailboxes and apps a fix will affect, the effect on each and how to prepare, before you apply it.
Remediation impact analysis →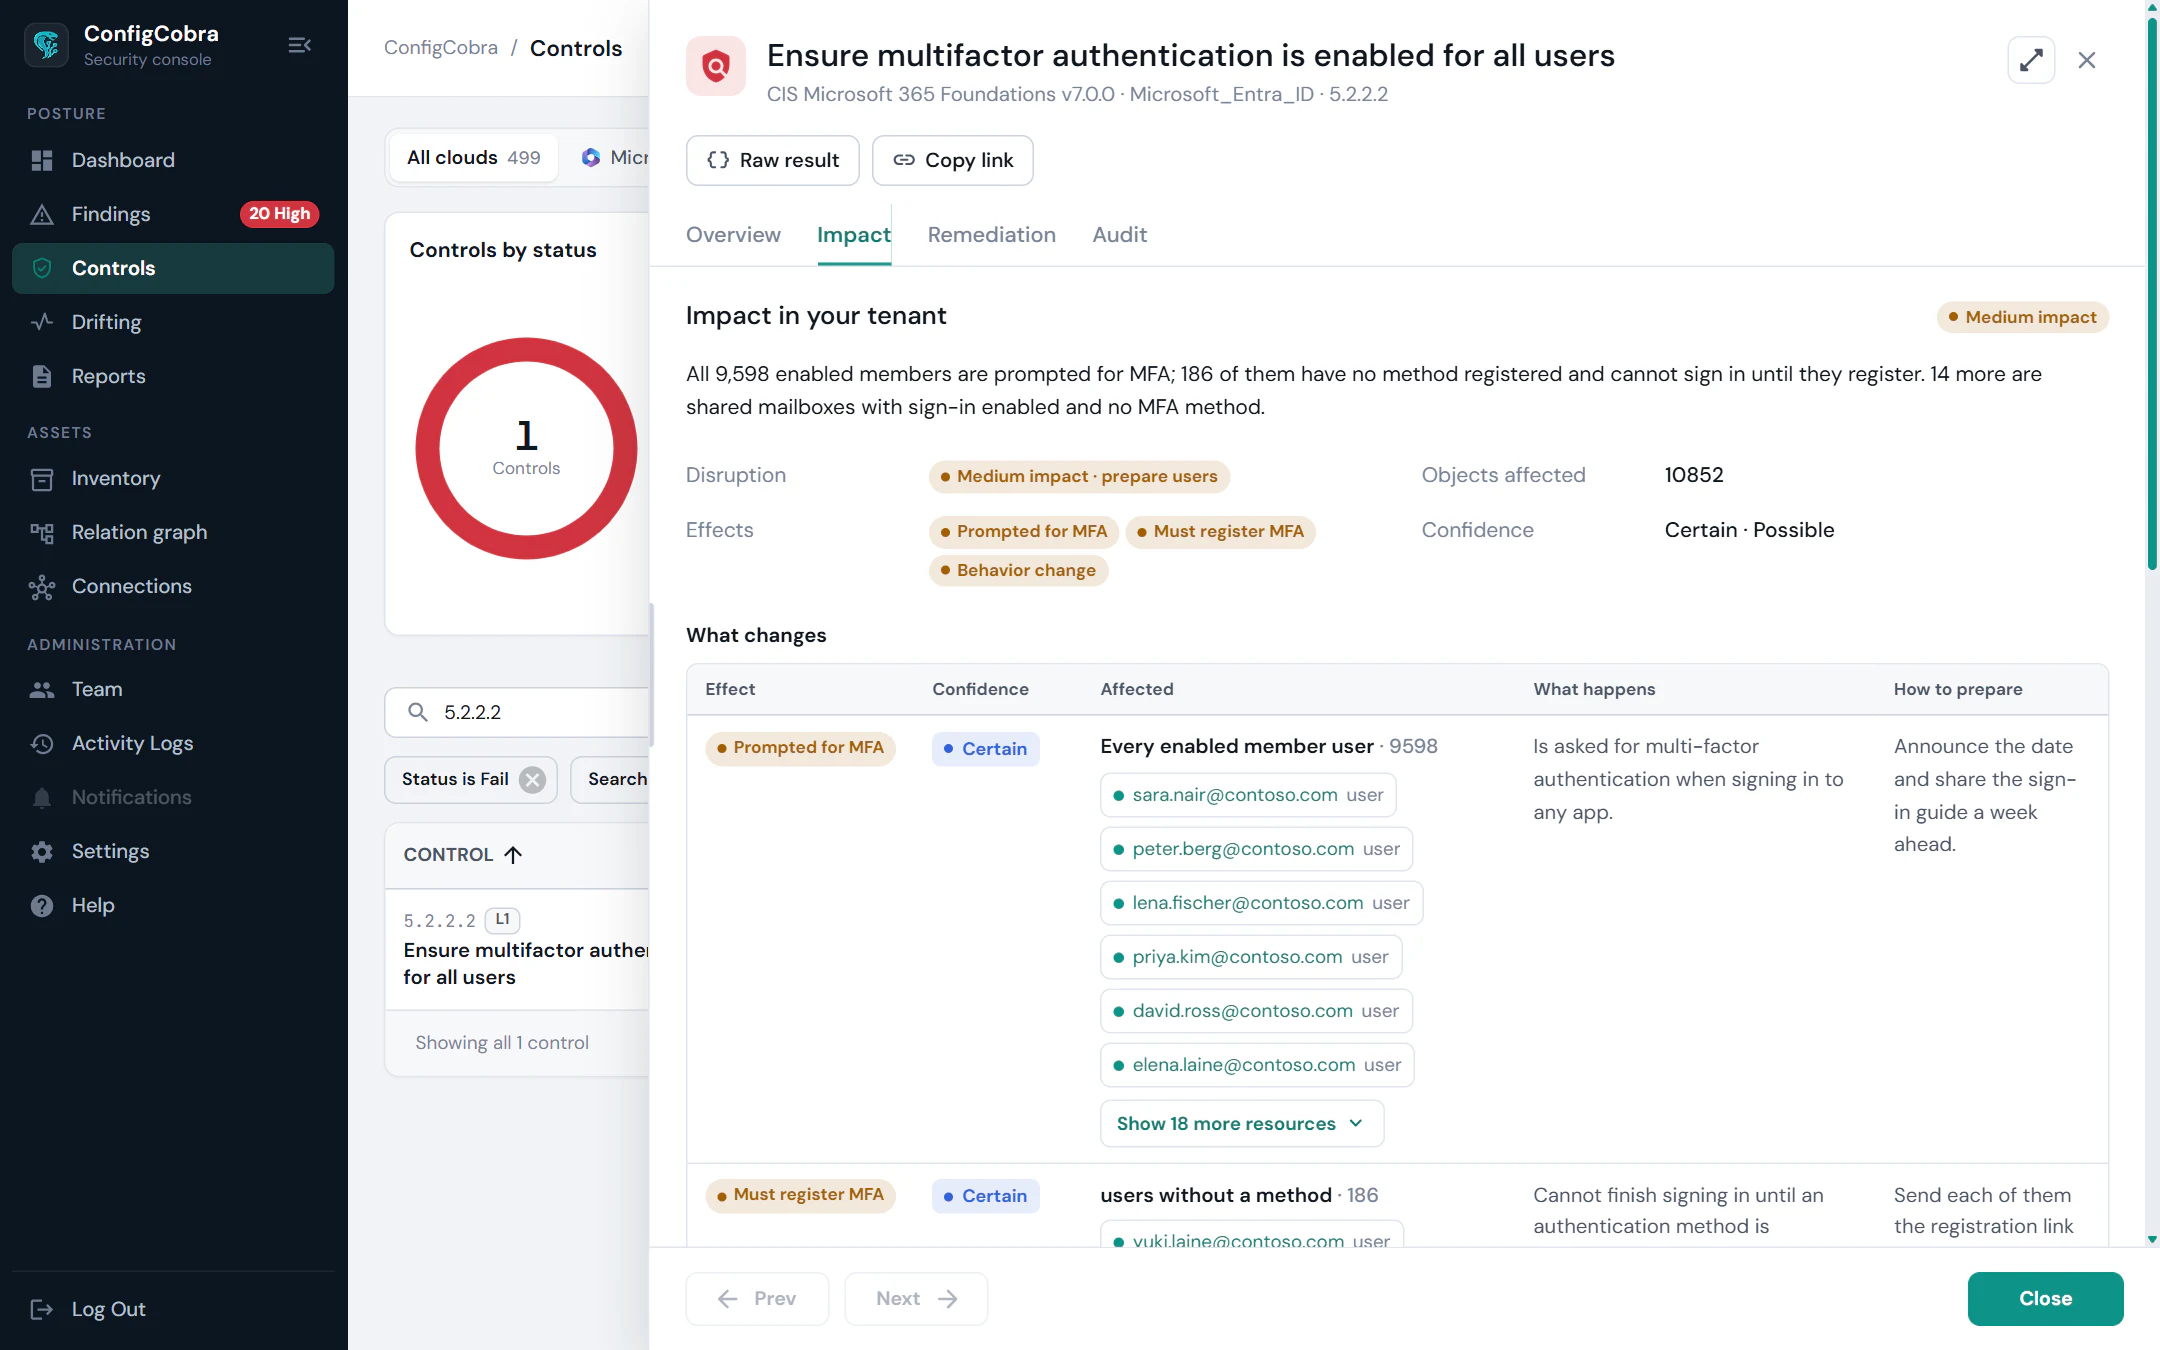
Dashboard
Your whole posture in one place.
A compliance score, the controls that pass and fail across every connected cloud, and the most severe failing controls first.
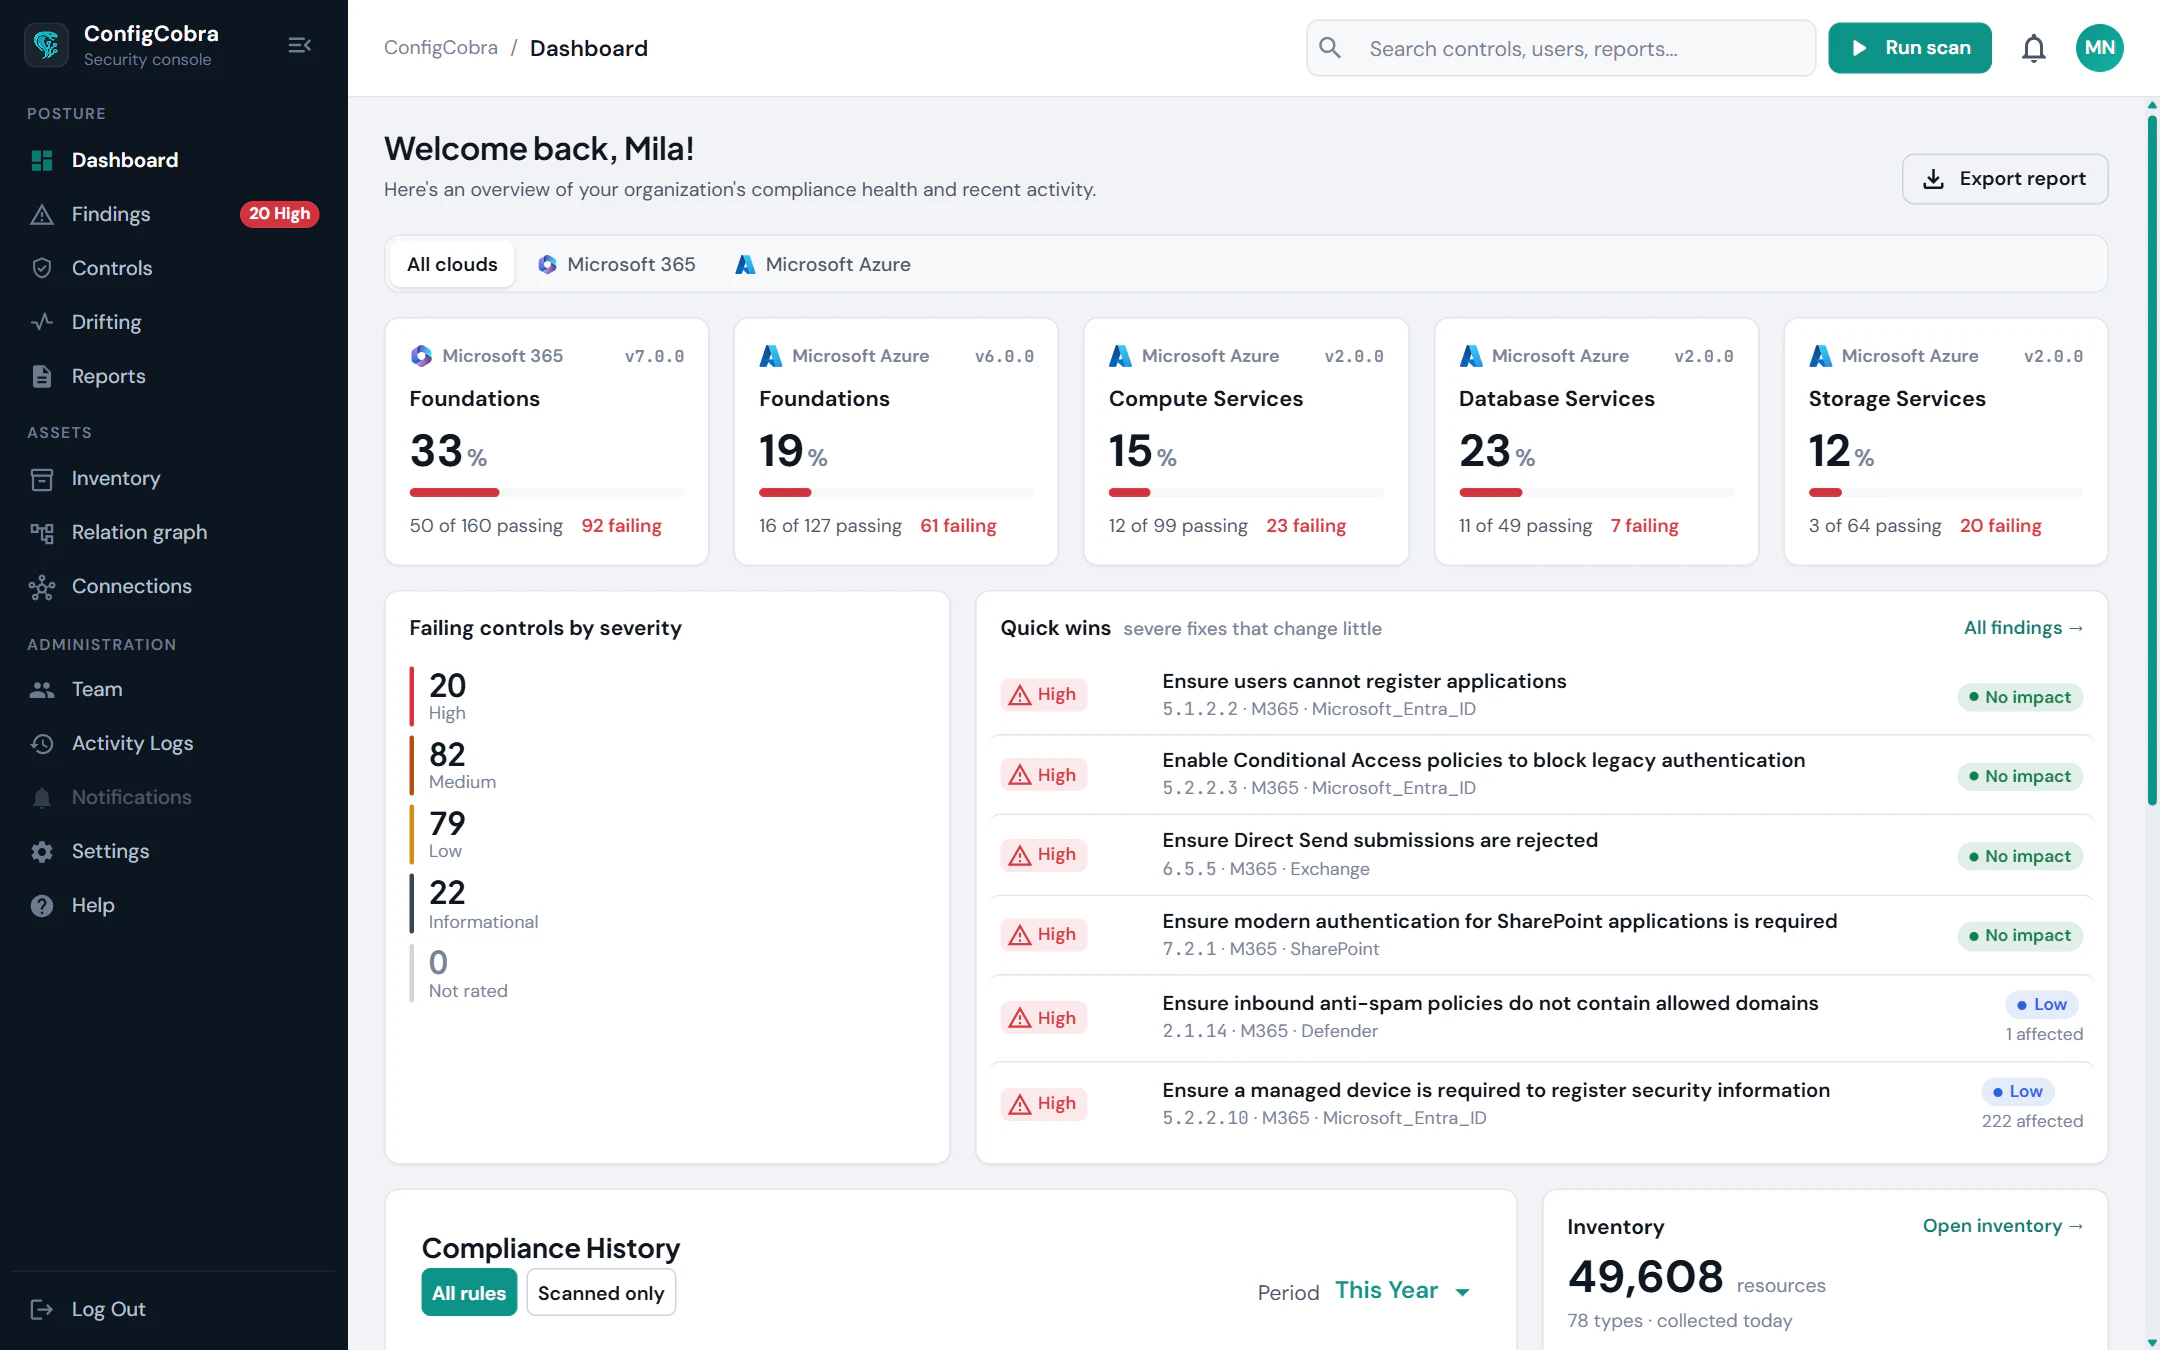
From the first scan to every tenant you manage.
Every connected cloud is scanned automatically every day, with ad hoc scans any time, and subsidiaries or client tenants are assessed from one workspace. Monitoring & drift →
CIS benchmark checks for every connected cloud
Evidence for every finding
Severity estimate per control
Posture dashboard
Multi-tenant workspace
Built on the CIS benchmarks.
- CIS controls checked today
- 898
- CIS benchmarks
- 10
- connectors live
- 4
Per-cloud benchmarks and control counts are on the connector pages.
Used in these solutions
Frequently asked questions
Which clouds and benchmarks does ConfigCobra CSPM cover?
Each connector is checked against the CIS benchmarks for that cloud. The connector pages list the exact benchmarks, versions and control counts, and which clouds are coming soon.
Where does the severity come from?
Severity is a ConfigCobra estimate used to prioritise remediation. CIS itself publishes no severity for its controls.
What access does ConfigCobra need?
Read-only access only. Each connector page lists the exact permissions it asks for. ConfigCobra never writes to your cloud; you run every fix yourself.
Can I try it for free?
Yes. The free trial runs for 14 days with full access to every control and module.
Try Cloud Security Posture Management (CSPM) on your own tenant.
Free trial: 14 days with full access. Read-only. Or see the whole platform.