Standards · Amazon Web Services
CIS AWS benchmarks.
306 controls, one scan.
The CIS Amazon Web Services Foundations Benchmark v7.0.0 plus the CIS AWS Compute, Database and Storage Services benchmarks, all assessed in one read-only AWS scan.
- Controls
- 306
- Benchmarks
- 4
- Access
- Read-only
- Connection
- Assume-role
Four benchmarks. 306 controls.
One AWS scan covers Foundations, Compute, Database and Storage Services.
What are the CIS AWS benchmarks?
The Center for Internet Security (CIS) is a non-profit organisation whose CIS Benchmarks are prescriptive configuration recommendations for hardening operating systems, cloud platforms and SaaS applications.
For AWS, the Foundations Benchmark is the broad baseline; CIS also publishes service benchmarks for AWS compute, database and storage services.
Benchmarks.
Control counts and the Level 1 / Level 2 split per benchmark.
CIS Amazon Web Services Foundations Benchmarkv7.0.0
CIS AWS Compute Services Benchmarkv2.0.0
CIS AWS Database Services Benchmarkv2.0.0
CIS AWS Storage Services Benchmarkv1.0.0
All 56 controls are Level 2.
Level 1 and Level 2.
- Level 1
Safe, minimal impact
Foundations 41 · Compute 72 · Database 93 · Storage 0. Baseline recommendations intended to be applied broadly with minimal impact on day-to-day use.
- Level 2
Stricter, security-focused
Foundations 29 · Compute 10 · Database 5 · Storage 56. For environments with higher security requirements. Some may affect functionality and warrant testing first.
How ConfigCobra assesses it.
ConfigCobra for AWS is available.
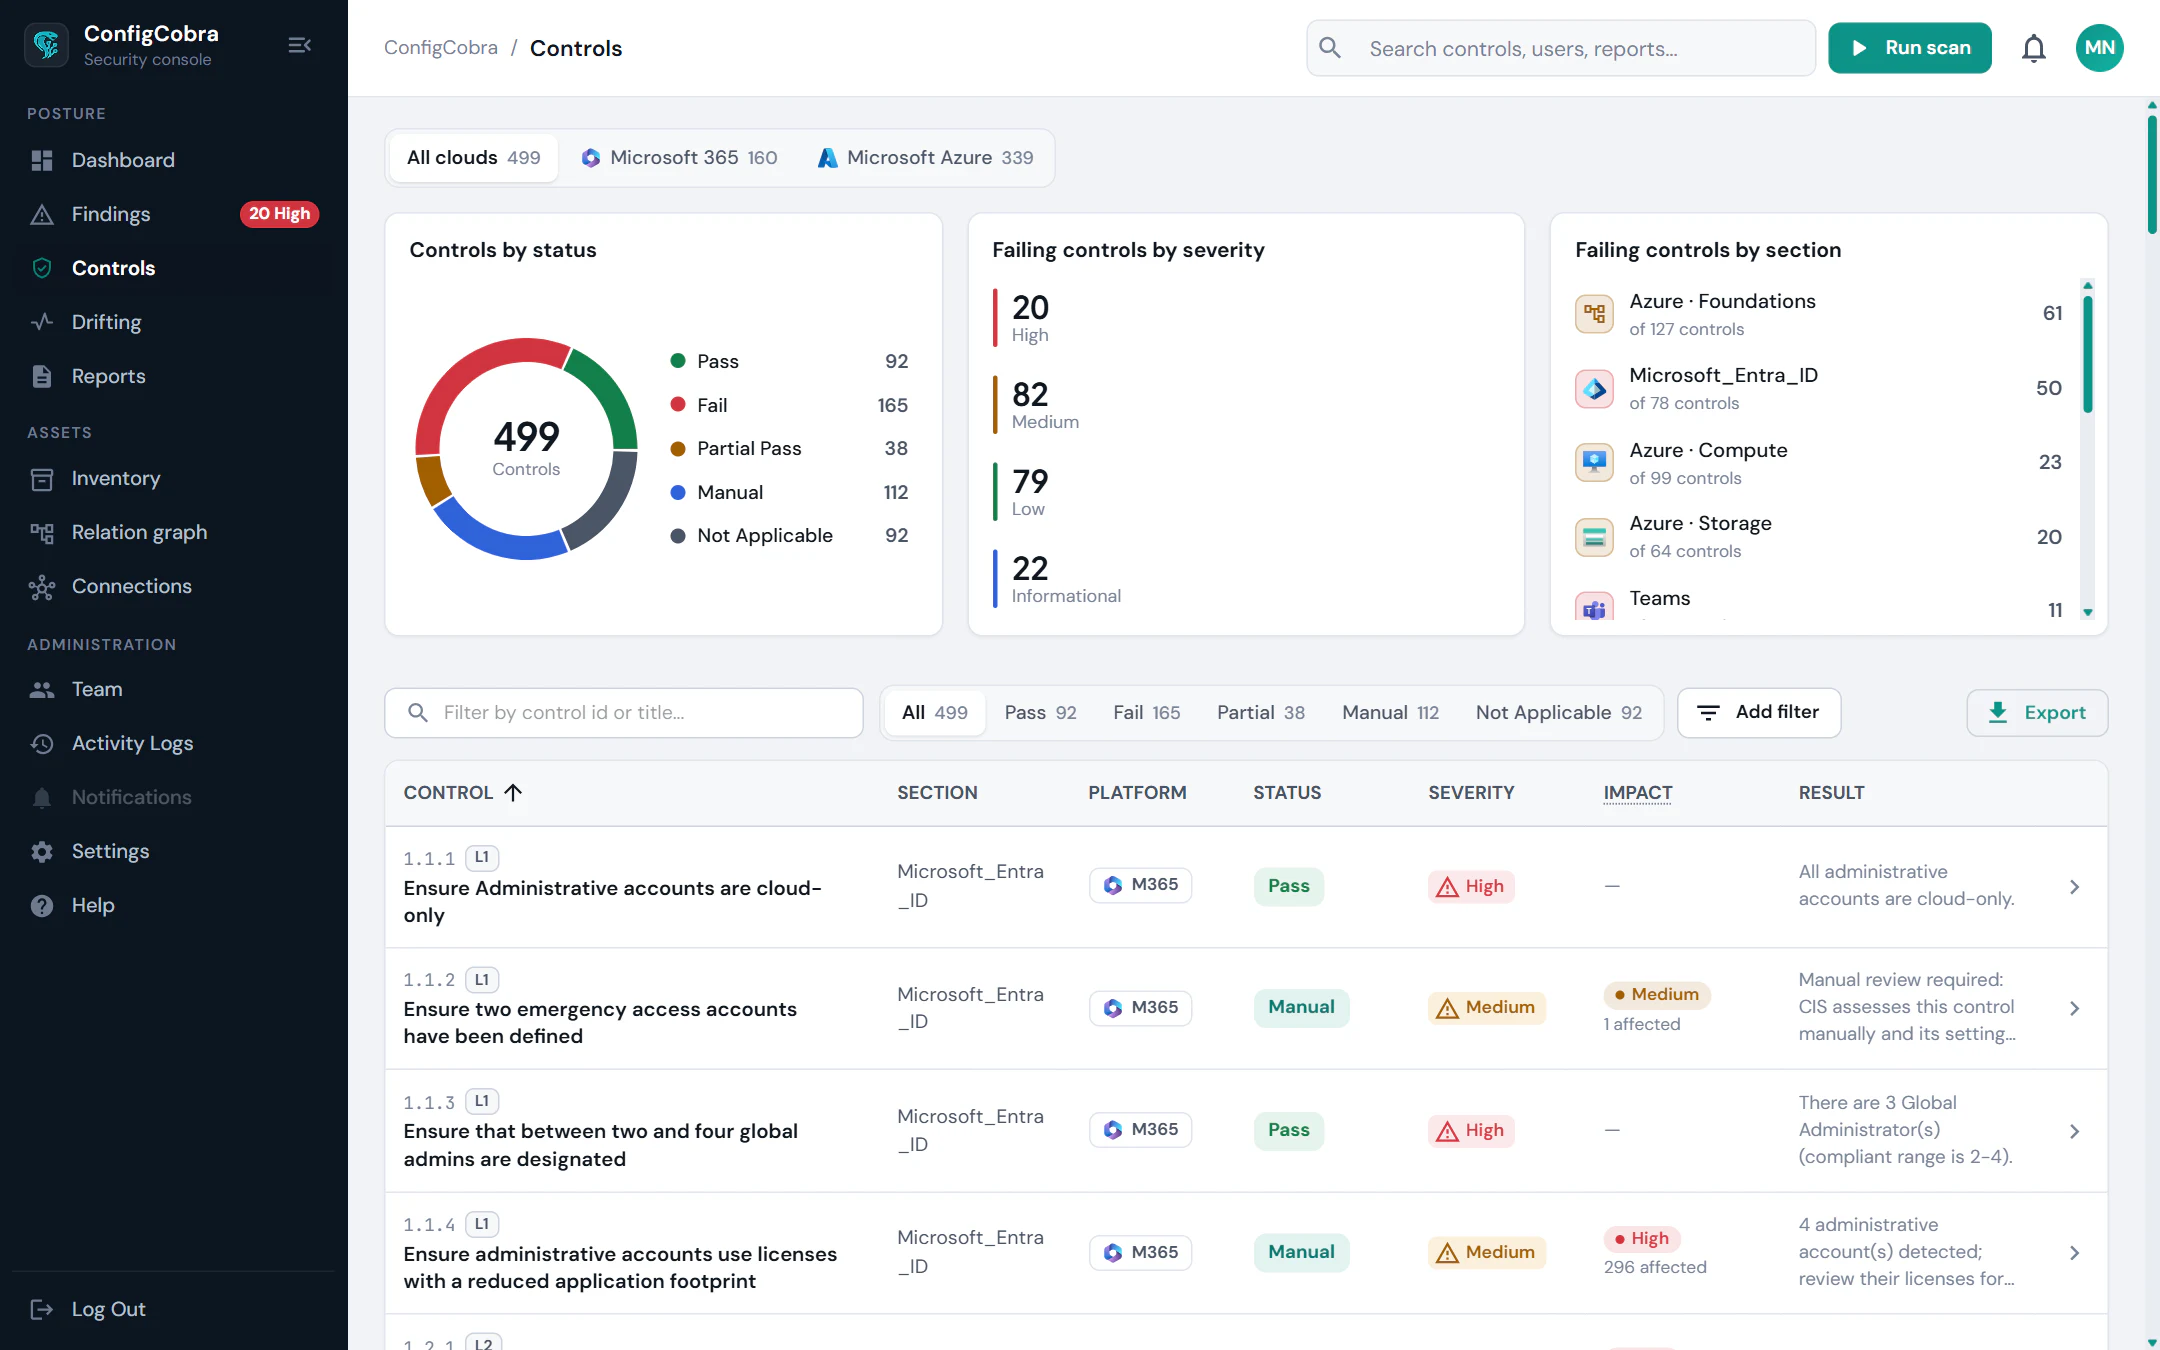
Scan
All four benchmarks in one scan.
Foundations, Compute, Database and Storage Services — 306 controls — assessed together.
Evidence
Every finding comes with evidence.
See the setting, what the benchmark expects and what the scan found, with a severity estimate per control to prioritise the fixes.
Cloud Security Posture Management →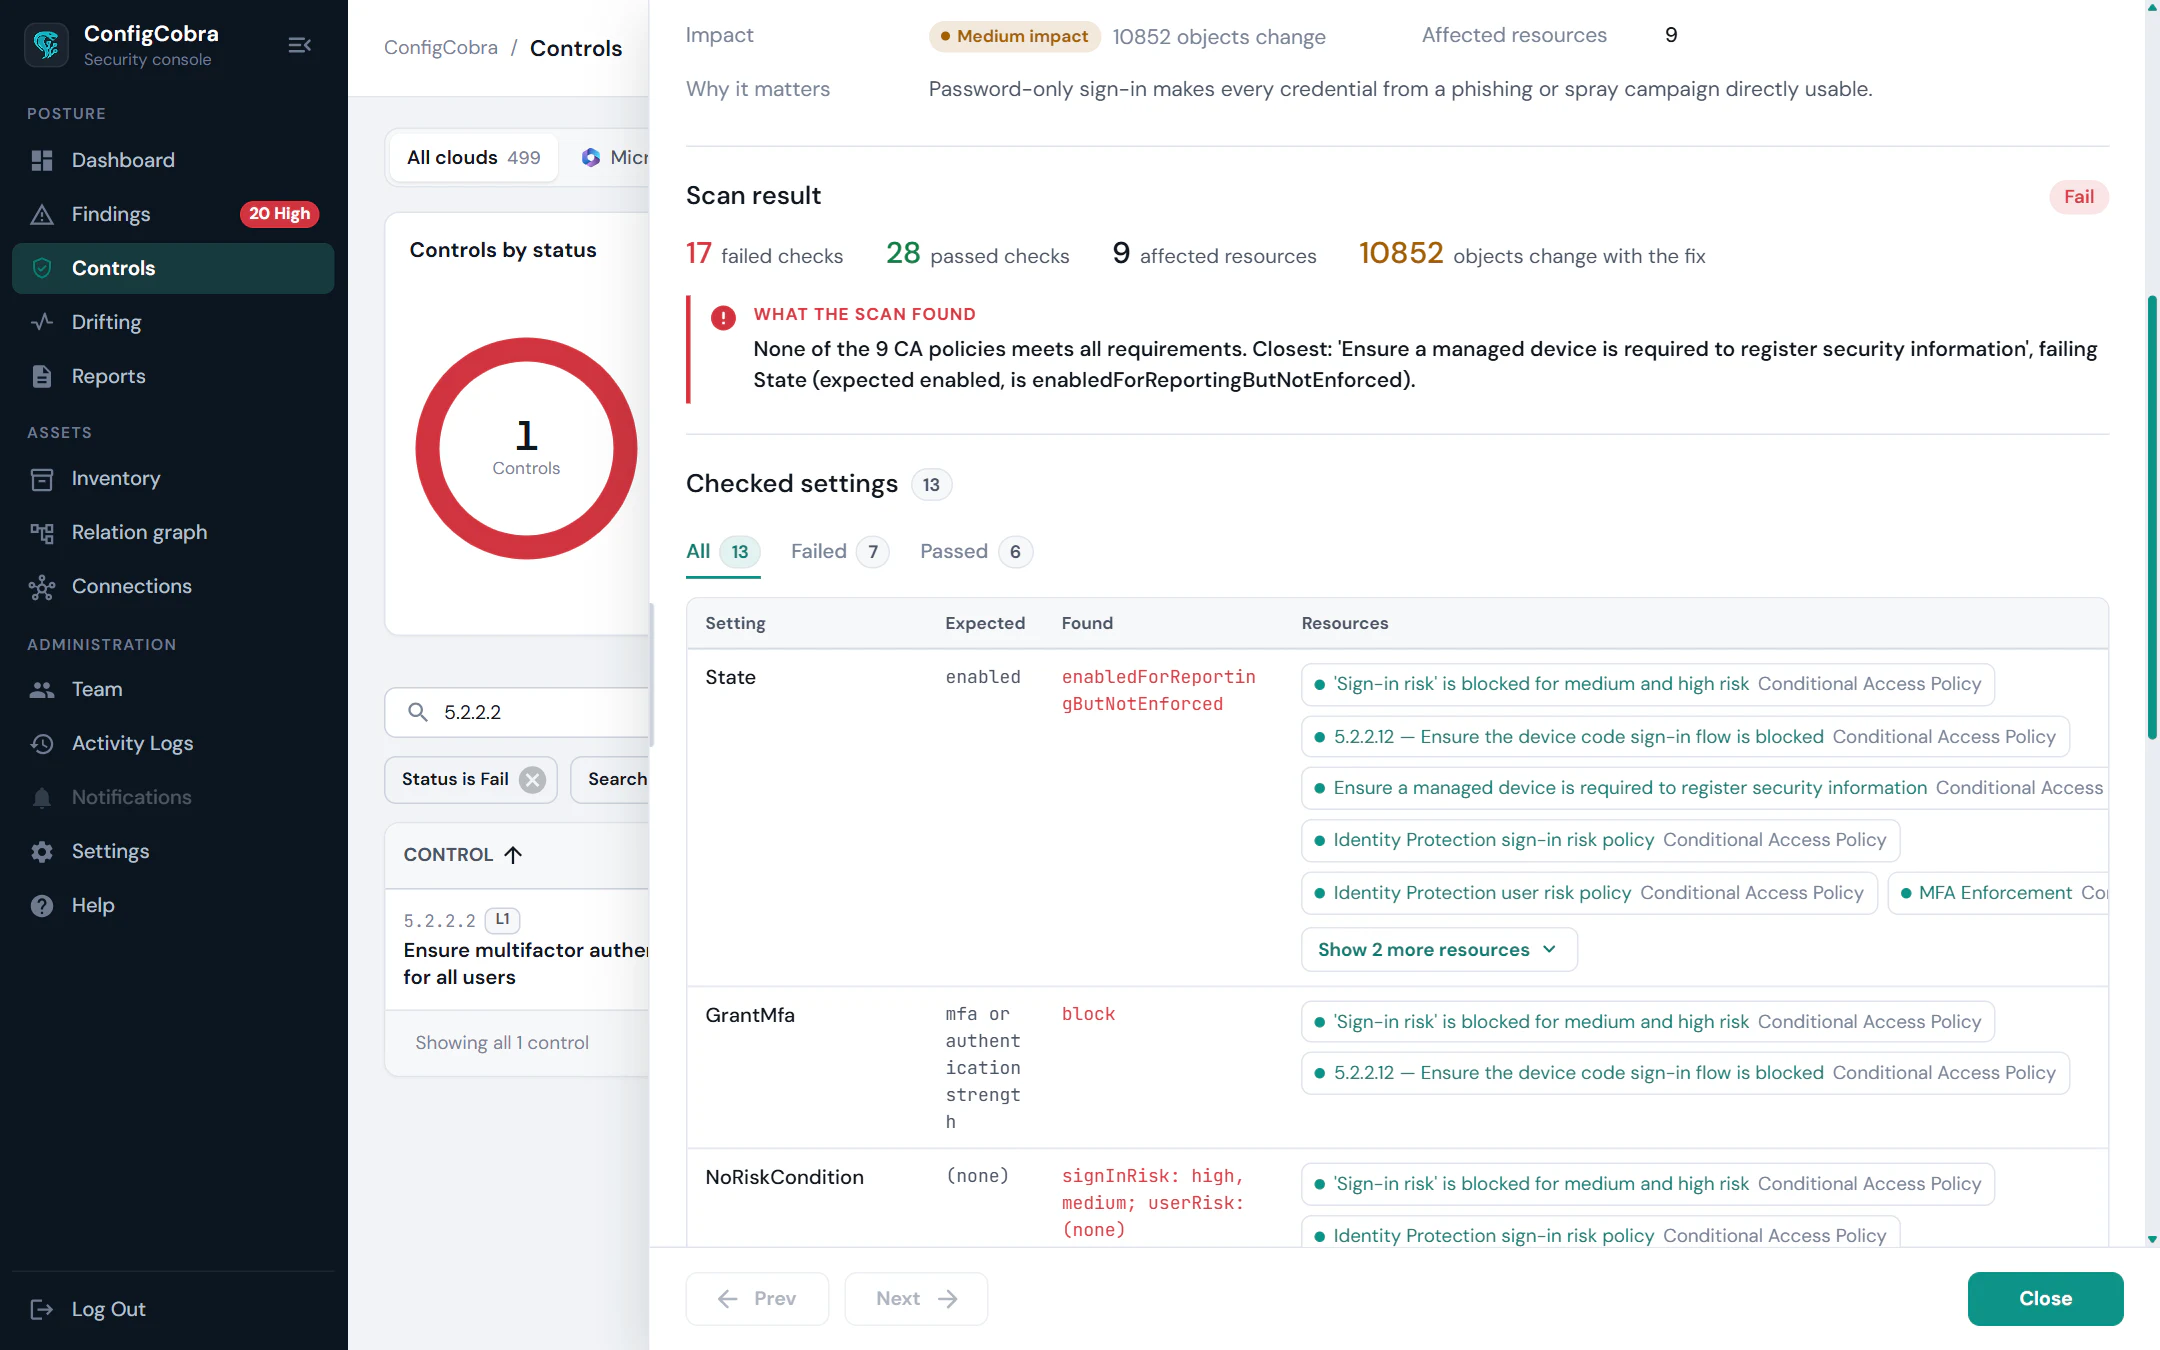
Read-only
Read-only access via assume-role. Never writes.
A read-only IAM role that ConfigCobra assumes, protected with an external ID.
ConfigCobra for AWS →Frequently asked questions
Which CIS AWS benchmarks does ConfigCobra cover?
CIS Amazon Web Services Foundations Benchmark v7.0.0 (70 controls), CIS AWS Compute Services Benchmark v2.0.0 (82), CIS AWS Database Services Benchmark v2.0.0 (98) and CIS AWS Storage Services Benchmark v1.0.0 (56) — 306 controls in total.
How many Level 1 and Level 2 controls are in each benchmark?
Foundations v7.0.0: 41 Level 1 / 29 Level 2. Compute Services v2.0.0: 72 / 10. Database Services v2.0.0: 93 / 5. Storage Services v1.0.0: 0 / 56.
Can ConfigCobra scan AWS today?
Yes. ConfigCobra for AWS is available. Start a free trial or ask us for a quote.
What access does the AWS scan need?
Read-only access through an IAM role that ConfigCobra assumes, protected with an external ID. It never writes to your AWS.
See it on your own tenant
Read-only access — ConfigCobra never changes your tenant.